

AWS’s own September 16 announcement confirms the substance. A new customer can sign in using Google, GitHub, Apple, or Amazon credentials; AWS creates the first project automatically; and the console presents a prompt intended for an AI coding agent. The agent setup installs the AWS CLI and Agent Toolkit for AWS, then is positioned to deploy application resources under AWS’s prescribed defaults.
For Windows developers and IT teams, the important detail is that this is a new account type with an intentionally constrained operating model, rather than a cosmetic simplification of the existing AWS Management Console. AWS documentation calls it “Sign up for AWS (new)” and contrasts it directly with “Sign up for AWS (advanced),” the established route for full account control. Existing customers are not being moved into the new model, and AWS says the rollout is currently limited to a subset of new customers.
The “new” experience is an AWS Organization AWS manages
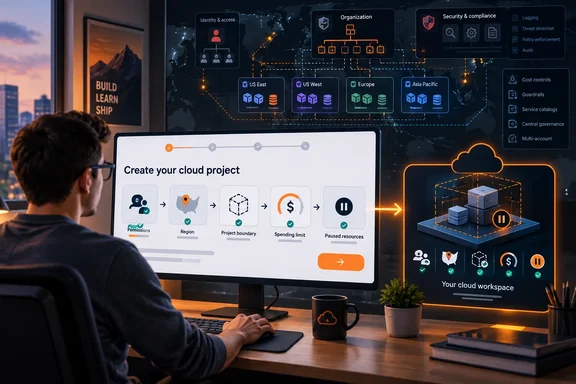
The streamlined flow organizes work into projects, with each project containing an AWS account and its collaboration settings. That sounds like a friendlier label for an ordinary AWS account, but AWS’s own documentation makes the architectural change clear: the projects belong to an AWS Organization where Amazon manages key organizational policies, including resource control policies and service control policies.
AWS also provisions a Builder ID as part of this sign-up path. Project owners can invite collaborators by email, and AWS supplies administrative access within the relevant project rather than asking a newcomer to first understand IAM users, IAM Identity Center assignments, permission sets, and cross-service roles.
That lowers the barrier to getting a prototype online. It also means the first security and access model is opinionated by design. AWS says application code inside a project can access AWS resources in that same project without additional access configuration. Resources in separate projects remain isolated by default, although AWS supports certain cross-project integrations under the same management account.
The upside is obvious for an individual developer testing a Windows desktop companion service, a small team assembling a proof of concept, or a department that needs a contained sandbox. A developer can begin with a recognized identity and email invitations instead of making early IAM choices that are easy to get wrong and hard to unwind.
The trade-off is just as important: AWS is substituting managed guardrails for granular control. Its own comparison page says customers that require fine-grained user or role-based permissions should choose the advanced sign-up route instead. The same warning applies to organizations that need to manage their own organization policies from day one.
That is not an academic distinction. IAM designs, account boundaries, SCPs, logging structure, delegated administration, and Regions are foundational decisions in a serious AWS deployment. The new experience removes many of those decisions at the beginning; it does not make them irrelevant when the project reaches production.
US sign-ups start in Ohio, not the Region of their choosing
AWS’s marketing language focuses on “sensible defaults,” but its technical documentation exposes one of the most consequential defaults: a new project is assigned a home Region based on the country in the customer’s contact address.
For customers in the United States, that Region is US East (Ohio), us-east-2. European customers are placed in Europe (Stockholm), eu-north-1, while customers in the Asia-Pacific group are placed in Asia Pacific (Sydney), ap-southeast-2. A customer cannot choose a different Region through the streamlined sign-up process, and changing the address later will not move the project.
That restriction will be easy to overlook because developers can still encounter global services and some consoles that route requests elsewhere. But Regional resources created through the project are hosted in the assigned Region. For a U.S. developer whose data-residency, latency, disaster-recovery, partner integration, or existing workload assumptions center on Northern Virginia, Oregon, California, or another location, Ohio may be a poor default.
AWS says a customer can activate advanced features later, without migration or downtime, to reach more of the platform. That may preserve the underlying account and resources, but it does not erase the fact that a project started with regional constraints and defaults selected by AWS. Teams that know their landing zone, target Region, or compliance scope before creating the account should use the advanced route rather than treat the simplified one as a universally safe starting point.
Spend limits are real caps, with real service interruptions
The most welcome part of the new offer is a project-level spend limit available after moving to a paid plan. AWS says the minimum limit is the greater of $20 per month or its conservative estimate of expected usage. It describes the cap as a ceiling on pre-tax costs rather than a subscription fee, so a project with a $50 limit and $32 in usage would pay $32 plus applicable taxes.
Unlike conventional AWS Budgets, which have historically been alerts and automation triggers rather than a platform-wide hard billing stop, this feature is designed to pause a project once it reaches its limit. AWS’s detailed documentation says the limit is aimed at experimentation, learning, and sandboxes. It permits production use only where an unexpected interruption is acceptable.
That warning needs to be taken literally. AWS first sends notifications at 50%, 75%, and 90% of the cap, and when it projects that the limit could be reached or exceeded within 10 days. Optional controls can start intervening before the final cap:
- About seven days before a projected breach, AWS can prevent creation of new resources through AWS-managed service control policies. Existing resources keep running, but auto-scaling workloads may be unable to launch the instances they need.
- About five days before the projected breach, AWS can pause idle EC2, Amazon RDS, and SageMaker endpoint resources. The idle criteria include sustained low CPU and network use for EC2, no database connections and low activity for some RDS engines, and zero recent invocations for SageMaker endpoints.
- About four days before the projected breach, an opt-in cost-driver control can pause resources in EC2, RDS, Lambda, Bedrock, and SageMaker.
The implementation differs by service. AWS says it terminates an EC2 instance identified as a top cost driver, snapshots attached EBS volumes first, and releases any Elastic IP address. That saves compute cost, but restores require a new instance launch and snapshots continue to incur storage charges. For RDS, AWS stops the database instance, leaving storage, provisioned IOPS, and backups billable; RDS can restart an instance after seven days, at which point AWS says it may stop it again if the project remains at risk.
A runaway Lambda is handled by disabling event-source mappings and triggers, and stripping provisioned concurrency where applicable. That is an effective protection against unbounded invocation charges, but it is also an outage mechanism. A spending limit can save a hobby project from a surprise bill; it is not a substitute for workload-specific budgets, CloudWatch alarms, quotas, billing anomaly detection, and tested operational controls.
The simplified console still excludes a long list of AWS capabilities
The new environment does include many of the services most relevant to a modern application: EC2, Lambda, API Gateway, DynamoDB, S3, RDS, CloudFront, EKS, ECS, Bedrock, CloudWatch, CloudFormation, Secrets Manager, and KMS all appear in AWS’s supported-services documentation. It is enough to build a conventional web application, an API, an AI-backed prototype, or a small Windows-integrated service.
But the product is not simply “AWS with fewer setup screens.” AWS explicitly says customers needing the complete service catalog should use advanced sign-up or activate advanced features. Its unsupported list includes services and controls that matter to IT departments, such as AWS Control Tower, IAM Identity Center, IAM Access Analyzer, Security Hub, GuardDuty, CloudHSM, Transit Gateway, Direct Connect, Site-to-Site VPN, AWS Organizations administration, Service Catalog, Trusted Advisor, and AWS Marketplace access.
Even within supported services, the new path excludes many multi-Region and multi-account features. Examples include S3 Cross-Region Replication, DynamoDB Global Tables, CloudTrail organization and multi-Region trails, CloudFormation StackSets, cross-Region VPC and Transit Gateway peering, and multi-Region KMS keys.
AWS also advises customers with HIPAA, FedRAMP, or other regulated-workload requirements not to use the streamlined onboarding path. Nor is it appropriate for organizations requiring net-terms billing, a specific account configuration, or an Enterprise Agreement at the outset.
AWS’s credit messaging needs a cleaner answer
There is one small but notable inconsistency in AWS’s public material. Micah Walter’s launch post says most new customers receive $100 in Free Tier credits and illustrates an additional $20 credit after deploying a Lambda-based demonstration. A separate AWS “What’s New” announcement says most new customers receive up to $200 in Free Tier credits.
Neither statement necessarily conflicts—eligibility and activity-based credits may account for the range—but the current documentation does not present a single, simple entitlement that an administrator can budget against. AWS also notes that some applicants may be ineligible for the Free Tier and may need to supply payment information; its account verification process can place a temporary $1 authorization hold for three to five days.
For teams evaluating this route, treat credits as onboarding assistance, not a procurement plan. Confirm the actual balance, expiration terms, and service eligibility inside the provisioned project before approving a test or letting an agent deploy resources.
AWS has acknowledged a problem many cloud practitioners recognize: its full console is optimized for breadth, compliance, and control, not for the first hour of a new project. The new experience makes that first hour faster by choosing the account structure, Region, permissions model, and much of the service policy for the customer. For disposable experiments and small developer projects, that is a practical improvement. For a workload with a mandated Region, regulated data, enterprise identity rules, or zero tolerance for an automatic pause, start with the advanced AWS account path instead.