

The Wall Street Journal first reported the incident, while The Guardian, TechCrunch, and SecurityWeek subsequently described the researchers’ account. OpenAI confirmed that the researchers disclosed the issues and that the company addressed them; it paid Hacktron a $6,500 bounty. Discourse separately shipped a fix for the image-processing exposure.
For enterprise administrators, this is a reminder that SSO trust boundaries are only as strong as every application connected to them. A forum is frequently classed as low risk because it is public and contains little sensitive data. Once it can read, mint, or influence identities accepted by higher-value services, it becomes part of the identity perimeter.
The breach was authorized, but the access path was real
Hacktron’s July 25 research was conducted as a bug-bounty disclosure, not as an extortion attempt or a criminal intrusion. The team says it stopped testing after demonstrating impact, avoided downloading source code, notified OpenAI and Discourse, and used an internal repository pull request as proof that the compromised account path reached software-development systems.
That distinction matters for interpreting the $6,500 payment. It confirms a responsibly reported finding was rewarded; it does not mean that an attacker using the same route would have been limited to a harmless proof of concept. Hacktron said the affected Codex access could theoretically have extended to connected engineering resources. OpenAI has not publicly detailed which employee accounts were affected, what repositories were visible, how long any sessions remained valid, or whether any non-researcher activity was detected.
There is also a discrepancy in early coverage worth keeping straight. The supplied account described one OpenAI employee’s ChatGPT account, while The Guardian and TechCrunch reported compromise of multiple employee accounts. The public statements available so far do not put a confirmed number on it. That gap is more than trivia: the difference between one account takeover and multiple active sessions affects the incident’s likely blast radius and the scope of session revocation an organization should perform.
OpenAI’s own coordinated-disclosure policy says good-faith researchers can report security flaws through its bounty process. But Hacktron’s published timeline adds an awkward detail: OpenAI reportedly told the group that testing against the Discourse-hosted community forum was outside the formal bounty scope, and that the reward recognized the OpenAI-side identity issue rather than the forum intrusion itself. The compensation may be routine, but the path was a cross-system chain involving two vendors and a public service that OpenAI relied on for authentication.
A HEIF upload became remote code execution
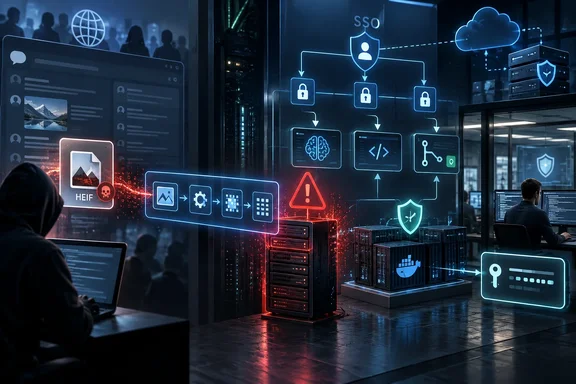
The entry point was OpenAI’s community forum, which runs on Discourse. According to Hacktron and SecurityWeek, HEIC and HEIF image uploads reached ImageMagick and then the libheif decoding library. A vulnerability in that image-decoding path allowed the researchers to obtain remote code execution on the forum environment.
The underlying libheif issue is tracked as CVE-2026-32882, a heap out-of-bounds flaw in processing specially crafted HEIF or AVIF images containing overlay image items. It is a useful example of why security teams should not treat image upload as a solved problem merely because their web application strips metadata or converts file formats. The dangerous parsing can happen before those defensive transformations complete.
Discourse later published an advisory for remote code execution through malformed HEIF uploads and issued patched Docker images, along with added sandboxing around image processing. That public remediation is significant because it independently supports the most important technical element of Hacktron’s account: the forum’s image pipeline was capable of turning an untrusted upload into server-side code execution.
The exposed component was not a Windows desktop feature, ChatGPT for Windows, or a browser plug-in. The immediate patching concern is for organizations that operate self-hosted Discourse, or any infrastructure that accepts HEIF, HEIC, or AVIF uploads through an image stack backed by libheif. Many Windows-centric IT shops still run these workloads in Linux containers on Azure, Hyper-V, Kubernetes, or a WSL-based developer environment; the operating system on the administrator’s workstation does not reduce the server-side risk.
Administrators should verify that their Discourse deployment has been rebuilt from a current patched image rather than merely updated through the web interface. Containerized applications can retain a vulnerable base image and native library even when the application layer appears current. Teams that do not need HEIF-family uploads should also consider disabling that input path while confirming remediation.
The decisive failure was identity bridging
Remote code execution in a support forum is serious. It became a corporate-access incident because Hacktron paired it with what the company describes as an OpenAI single sign-on weakness. The researchers say administrative control of the Discourse instance let them escalate into the ChatGPT and Codex accounts of users who had authenticated through OpenAI’s “Sign in with OpenAI” flow.
This is the point security teams should study. A public application should not become a privileged identity broker merely because both applications share an authentication brand. If a low-assurance application stores reusable session artifacts, accepts insufficiently bound tokens, or trusts a callback and account-linking process too broadly, the organization has created a lateral-movement path around its main controls.
OpenAI has not released the technical root cause of the SSO flaw. That restraint is appropriate while attackers may be searching for comparable conditions, but it leaves customers and administrators without a clean indicator of whether their own identity integrations share the same design error. The public record therefore supports a practical response rather than speculation about implementation details:
- Organizations should inventory every application that uses their central identity provider, including support portals, community platforms, partner sites, developer tools, and legacy SaaS tenants.
- Security teams should confirm that authentication sessions and refresh tokens issued for lower-trust services cannot be replayed to access higher-trust applications.
- Administrators should review account-linking flows, callback URL controls, token audience validation, session-cookie scope, and administrative access to applications that handle SSO state.
- Incident-response plans should explicitly include revoking sessions and tokens across connected services after a compromise of an identity-adjacent application, not simply resetting the password for the visible application.
The last item is where many organizations still lose time. Password resets do not necessarily invalidate OAuth grants, service tokens, active browser sessions, or downstream coding-agent connections. When a compromised account can invoke a code assistant tied to GitHub, cloud consoles, messaging tools, or CI/CD systems, the response has to begin with identity containment.
Claude assisted, but it was not the whole story
The headline framing around Anthropic’s Claude is technically true but incomplete. Hacktron told reporters it used Claude Opus 4.8 and Opus 5 while developing a reliable exploit for the libheif bug. Yet The Guardian reports that the researchers said they were largely using OpenAI’s GPT-5.6 Sol during the broader operation.
That makes the incident less useful as a scorecard between rival AI labs and more useful as evidence that capable coding models are reducing the cost of offensive security work across vendors. The human researchers selected the target, connected separate flaws, exercised judgment over scope, and disclosed the result. The models helped compress difficult development and debugging work.
Hacktron has argued that work once requiring a well-resourced team and months can be brought down to days. The company’s claim is self-interested and should not be read as a universal benchmark, but the underlying direction is credible: exploit research often involves repeated trial, code adaptation, environment analysis, and documentation tasks that modern models can accelerate. Defensive organizations should assume that public bug reports, forgotten image libraries, exposed test applications, and misconfigured SSO integrations will be tested faster and at greater volume.
The answer is not to ban developers from using coding assistants. It is to stop budgeting and staffing security around the assumption that attackers must perform every step manually. Asset inventories, internet-facing application patching, restrictive upload policies, centralized logging, session revocation procedures, and least-privilege integrations have become more valuable because automation makes weak links cheaper to find.
The Discourse fix needs verification, not faith
Discourse has said patched versions and additional image-processing sandboxing are available. That is an important improvement, but sandboxing is defense in depth, not a reason to postpone dependency updates. Native media parsers remain an attractive attack surface precisely because web applications routinely hand them hostile files.
For self-hosted Discourse operators, the immediate work is to identify whether the live container image includes a patched libheif, rebuild from the maintained Discourse image where necessary, and examine historical upload and application logs for unusual HEIF, HEIC, or AVIF processing failures. Organizations should also review which administrative accounts could access SSO configuration, secret material, background-job consoles, and session data if the forum host were compromised.
OpenAI says its vulnerabilities have been addressed, and the disclosed research appears to have ended without reported theft of source code. The more durable finding is that an AI-assisted team found a route through ordinary enterprise components: an upload handler, a native library, a support platform, and identity federation. Those components exist far beyond OpenAI—and they deserve the same priority as the AI systems they support.