

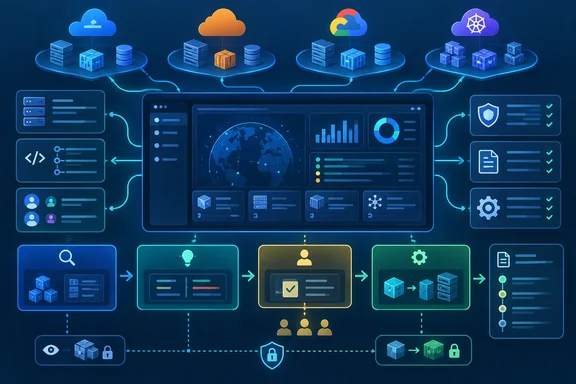
For platform teams, the important question is not whether another tool can spot infrastructure drift. It is whether that tool can distinguish an unauthorized change from an emergency fix—and choose an appropriate response without turning a configuration discrepancy into an outage.
A shared picture of code, resources and policy
EZ Control follows the March 2026 merger of env zero and CloudQuery. Env zero says the service combines discovered infrastructure with code-declared state through more than 80 integrations, covering nearly 2,300 resource types. Its context layer links resources to owners, repositories, costs, dependencies, policies and risks. Those coverage numbers are vendor claims, not independently benchmarked results.
The proposed scope extends beyond infrastructure-as-code, or IaC. Env zero says EZ Control can consume intent from security-posture rules, policy repositories and cloud-provider guardrails, addressing security, compliance, cost, maintenance, availability and performance requirements.
That distinction matters when evaluating the product: matching the repository is not necessarily the same as meeting every operational requirement. A useful trial should test those separately rather than treating a clean drift report as a universal certificate of good health.
Four levels of authority—not one autonomy switch
According to VMblog’s account of the announcement, teams can select authority by resource class:
- Observe only
- Propose a fix
- Act with approval
- Act autonomously within defined guardrails
Env zero says these choices are policy-based rather than product-tier restrictions. Its announced responses include reapplying IaC for accidental drift, proposing repository changes for intentional modifications, and flagging source-code defects. Other violations use the remediation defined by their governing policy, followed by a verification scan.
The practical evaluation question is how the system establishes which response is appropriate. Consider a hypothetical administrator who changes a production configuration during an incident. Should the controller restore the repository’s version, preserve the emergency change through a pull request, or wait for approval?
A sensible acceptance test would require evidence for that decision: the owning team, applicable exception, proposed change, approval record and resulting resource state. “Autonomous” should describe bounded execution, not permission to guess.
Azure already has remediation capabilities
The launch’s suggestion that existing governance stops at alerts needs qualification. Azure Policy already supports remediation of existing noncompliant resources through policies with modify or deployIfNotExists effects. Microsoft documents remediation tasks that execute those operations using a managed identity associated with the policy assignment.
Microsoft also specifies that the identity needs the appropriate Azure role-based access control permissions and recommends restricting those permissions to the smallest necessary set. Changing a policy definition does not automatically update its assignment or associated managed identity.
Consequently, EZ Control’s proposed distinction is not simply “remediation exists.” It is the claimed coordination of discovered assets, repositories, ownership and policies across environments. Azure administrators should ask how it interacts with existing remediation tasks, exceptions and deployment workflows—not assume it replaces them.
That comparison also exposes an important procurement question: which identity actually performs each change, and what can that identity access?
AI-agent governance remains a claim to validate
Env zero says AI agents can operate under the same policies, approvals and audit trail as engineers without receiving raw cloud credentials. However, the announcement does not explain the credential architecture or authorization boundaries. It also describes actions as reversible without detailing rollback mechanisms for individual operations. These are stated product properties, not demonstrated guarantees.
For a pilot, require a demonstration of:
- An action blocked because it exceeds the agent’s permitted scope.
- An approval-required action that cannot bypass review.
- An audit record connecting the request, authorization and execution.
- Recovery from a failed or partially completed change.
Those are suggested evaluation criteria, not documented EZ Control setup steps. A post-change compliance scan is useful, but buyers should separately define what constitutes successful recovery and healthy application operation.
Start with discovery, then earn write access
Env zero says initial connection is agentless and read-only, with authority increased selectively by resource class. That starting boundary is more consequential than the launch’s AI-era branding: organizations can evaluate discovery before authorizing remediation.
Keep the first trial focused on inventory accuracy, ownership mapping and policy interpretation. Before enabling writes, request integration-specific permissions, approval behavior, rollback limitations, data-handling terms and commercial conditions. The announcement does not establish pricing or a general-availability timetable.
EZ Control offers a concrete governance model worth evaluating. The standard for success, however, should be equally concrete: not how confidently it proposes a fix, but how reliably it stays inside the authority an enterprise actually granted.
References
- env zero Launches EZ Control, the Autonomous Cloud Control Plane for the AI Era - VMblog VMblog · Thu, 01 Oct 2026 18:11:32 GMT
- env zero Launches EZ Control, the Autonomous Cloud Control Plane for the AI Era | env zero envzero.com
- Remediate non-compliant resources - Azure Policy | Microsoft Learn learn.microsoft.com