

Microsoft’s hybrid identity documentation provides an important reality check. Connecting identity systems does not make them interchangeable, synchronization is not automatically bidirectional, and shared infrastructure can weaken intended security boundaries. Unified visibility and unified enforcement are different achievements. Microsoft’s documented synchronization and tenant-isolation models illustrate why both need separate validation.
What identity fabric actually connects
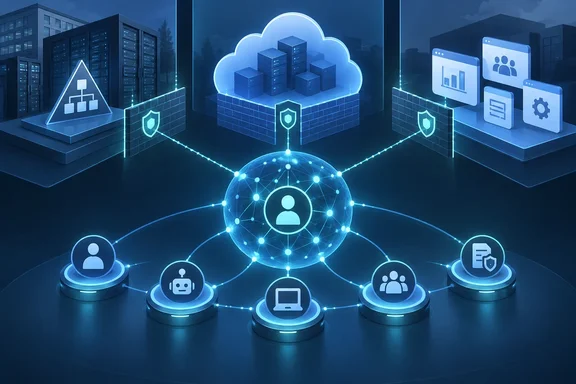
SC Media describes four architectural elements: identity sources, an identity graph, access proxies and policy engines. The graph relates people, service accounts, devices, resources, groups and policies, allowing access relationships to be examined across systems. Its proposed capabilities encompass identity aggregation, protocol integration, contextual authorization, lifecycle management and observability.
That is an architectural description, not evidence that every implementation supplies every capability. The distinction matters particularly for legacy applications: Microsoft documents specific integration requirements for Application Proxy and SAML single sign-on, rather than a universal translation layer that makes any authentication mechanism work with any other.
An administrator should therefore ask two different questions:
- Can the identity layer discover and correlate this account’s access?
- Can a supported integration enforce the intended policy at the application?
This is the central analytical distinction: a relationship map can inform a decision, but the application’s access path still needs a functioning enforcement mechanism. NIST’s multi-cloud zero-trust guidance similarly discusses application and service identities alongside gateways and enforcement infrastructure—not identity information in isolation.
Synchronization needs an owner, not just a connector
Microsoft’s Microsoft 365 identity-model guidance describes a conventional hybrid arrangement in which accounts originate in Active Directory Domain Services and have corresponding objects in Microsoft Entra ID. In that documented model, most changes flow from AD DS to Entra ID, with exceptions for particular attributes. AD DS remains the authoritative source for the account information.
That directly qualifies the idea that an identity fabric inherently provides bidirectional synchronization. Directionality is a property of the configured integration, not a benefit conferred by the architectural label. Microsoft’s Cloud Sync documentation, for example, describes both AD-to-Entra synchronization and particular cloud-to-AD provisioning scenarios, including group provisioning. Those capabilities do not establish unrestricted write access across every connected directory.
A useful planning artifact is an attribute-authority matrix. Based on those documented boundaries, administrators should record:
| Planning question | What to establish |
|---|---|
| Where does an account originate? | The system responsible for creating and maintaining it |
| Who owns each synchronized attribute? | Which system is permitted to change that value |
| What flows back? | Explicitly supported writeback or provisioning scenarios |
| Which objects are included? | Connector scope, filters and exclusions |
| What happens after a failed update? | Monitoring ownership and the recovery procedure |
This matrix is an implementation recommendation synthesized from Microsoft’s synchronization guidance, not a Microsoft-mandated template. Its purpose is to prevent an apparently unified identity from having several competing sources of truth.
Legacy applications still have prerequisites
Microsoft Entra Application Proxy provides a concrete example of extending cloud identity controls to on-premises applications. Microsoft recommends it for remote access to internal resources and cautions against using it for intranet access because the additional path can introduce latency. It requires Microsoft Entra ID P1 or P2 licensing.
Two supported integration patterns show why application-level discovery remains necessary:
- Kerberos Constrained Delegation: Microsoft requires the connector server and application server to be domain-joined and located in the same domain or trusted domains.
- SAML single sign-on: The application must consume SAML tokens issued by Microsoft Entra ID. Microsoft’s documented configuration does not apply to applications that retain an on-premises identity provider.
For the SAML pattern, Microsoft recommends first establishing and testing single sign-on on the corporate network. After publishing the application through Application Proxy, administrators must align the external-facing SAML configuration, including the reply URL, and test access with an assigned account. Successful publication alone is not proof that the complete sign-on flow works.
Microsoft’s deployment guidance also recommends at least two connectors per connector group for availability and scale, plus TLS between the connector and the target application. These are concrete operational requirements that an architecture diagram cannot replace.
The takeaway: modern identity controls can extend the useful life of compatible legacy applications, but “no application changes required” should be treated as something to demonstrate for each application—not assume for the estate.
Unification must not erase isolation
Microsoft’s tenant-estate guidance identifies a particularly important hybrid identity risk: separate cloud tenants can still share an underlying security dependency. A compromised on-premises account synchronized into multiple tenants may affect those tenants, while improperly scoped on-premises group memberships may grant access across intended boundaries.
Microsoft recommends reviewing synchronization scopes, group-management practices, device-management boundaries and on-premises administrative privileges. It also advises aligning cloud isolation with the underlying Active Directory infrastructure.
For administrators evaluating an identity fabric, the analytical consequence is straightforward: correlating identities must not silently expand their authority. A connected identity architecture should make trust boundaries explicit, not turn every directory relationship into an access relationship.
A useful review question is whether the organization can explain how a change to an on-premises group affects access in each connected tenant. If that explanation is uncertain, expanding integration should wait until the scopes and ownership are understood. This recommendation follows Microsoft’s documented warning about shared identity sources and group memberships.
Choosing an approach without buying the label
SC Media organizes implementation into federation, selective consolidation and a graph-centric model. It identifies cloud migration, mergers, zero trust, audit reporting and developer access as potential uses, with synchronization freshness, proxy placement, policy complexity and performance as planning concerns.
Microsoft Cloud Sync supplies one concrete example relevant to that scope: it supports synchronizing multiple disconnected Active Directory forests into a single Entra tenant without first consolidating the forests. Microsoft also documents multiple active provisioning agents for availability. This demonstrates a useful integration capability; it does not prove that an organization has implemented the complete identity-fabric architecture.
A practical evaluation should therefore start with an outcome:
- Which access relationship is currently difficult to establish?
- Which application needs a supported enforcement path?
- Which source-system change must reach which destination?
- Which boundary must remain isolated?
These questions are a synthesis of Microsoft’s synchronization, application-integration and isolation guidance. They provide a more testable starting point than asking whether a product deserves the “fabric” label.
Standards support the objectives, not the branding
For compliance planning, NIST Cybersecurity Framework 2.0 provides a more direct identity mapping through PR.AA, its Identity Management, Authentication, and Access Control category. PR.AA-01 addresses managing identities and credentials; PR.AA-05 addresses defining, managing, enforcing and reviewing permissions, including least privilege and separation of duties. These are outcomes to demonstrate, not a prescription to purchase a graph-based architecture.
NIST SP 800-207A is also directly relevant to the multi-cloud portion of the discussion. It addresses identity-based application and service access policies and supporting infrastructure such as gateways and sidecar proxies. It does not validate SC Media’s three approaches as a standardized identity-fabric taxonomy.
SC Media’s predictions about machine learning, cloud-security signals and API-first designs should likewise be read as forecasts, not established implementation requirements.
The bottom line
Identity fabric is a useful architectural lens when it helps an organization explain and control access across distributed systems. Microsoft’s documentation shows both the opportunity—hybrid synchronization and supported legacy-application integration—and the limits: authority, compatibility, availability and isolation remain explicit engineering responsibilities.
For Windows and enterprise IT teams, the strongest evaluation criterion is not how many systems appear in one console. It is whether the organization can trace an access decision, enforce it through a supported path, and preserve the boundaries it intended to protect. A fabric should connect the pieces—not sweep the loose threads under the dashboard.
References
- Identity fabric: unifying identity across hybrid and multi-cloud environments - SC Media SC Media · 2026-10-01T14:58:18+00:00
- CSF 2.0 Core With Withdrawn CSF 1.1 Elements nist.gov
- What is hybrid identity with Microsoft Entra ID? - Microsoft Entra ID | Microsoft Learn learn.microsoft.com