

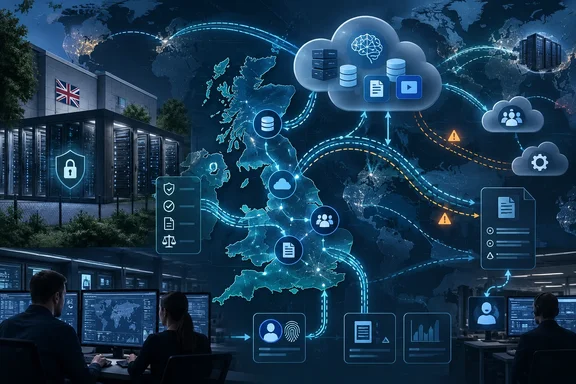
That distinction has direct consequences for Microsoft 365, Azure, Copilot and custom AI deployments. A tenant can have an approved regional data location while prompts, identity data, telemetry, logs, support-case information, connected third-party services or cross-tenant collaboration create paths that need separate review. The survey is vendor-sponsored and does not establish how widespread any individual configuration is, but its central warning matches the technical reality documented by both Microsoft and the UK Information Commissioner’s Office: residency is one control, not a complete sovereignty strategy.
The UK figures are a signal, not a market census
The underlying research is IDC’s Enterprise Horizons 2026: Where Innovation Meets Reality InfoBrief, commissioned by Expereo. Expereo says the global study covers 800 enterprise IT leaders in Europe, the United States and Asia-Pacific, and its September 15 announcement reports that 53% globally seek more control of sensitive and strategic data, 33% put digital sovereignty at a top or high priority, and 30% see it as a leading technology-investment driver.
TechRadar’s UK breakout is lower on each of those measures: 50%, 29% and 27%, respectively. It also reports that 26% of UK organisations are being pressed by customers or partners to localise data, and that 56% of UK technology leaders fear AI will introduce new security risks. Expereo’s global release puts the comparable risk figure at 54% and the customer-or-partner pressure figure at 22%.
Those differences may simply reflect country-level responses rather than an error; the published material does not provide the UK respondent count, the fieldwork dates, industry mix, confidence intervals or the exact wording used for the country questions. That omission limits how far readers should take the percentages. A small UK subsample can be a useful directional finding, but it should not be read as a precise measure of the entire British enterprise market.
The broader point has stronger support than the individual country numbers. IDC’s own 2026 writing on European sovereignty says buyers are increasingly focused on protection from extraterritorial data requests, regulatory compliance, privacy, security and operational dependency—not merely political symbolism. AI makes those questions more urgent because it joins data sources, model endpoints, retrieval systems, identity platforms and monitoring tools that may each operate under different geographic and contractual conditions.
Data residency does not tell administrators where every transfer goes
Microsoft’s EU Data Boundary documentation is unusually explicit about the limits of a location-based assurance. The company says its boundary is designed to store and process defined customer and personal data for covered enterprise online services within the EU and EFTA area. It also identifies circumstances in which some data may still transfer outside that boundary, including particular service capabilities, support and service-management scenarios, and network transit used for latency and resiliency.
Microsoft notes that variable network paths can occasionally route customer traffic outside the boundary. It also says limited pseudonymised personal data in service logs and professional-services support information can be consolidated globally for operational and quality-management purposes. Those are not necessarily compliance failures; they are documented service behaviours. But they mean a procurement statement saying “our Microsoft data is in Europe” does not answer every question a DPO, CISO or customer assurance team may ask.
The same applies to identity. Microsoft’s Entra documentation says that tenant location influences where most customer data is stored and processed, while also listing exceptions for data egress and optional features. Cross-tenant collaboration and multitenant administration can introduce processing involving another tenant’s location. Application Proxy configurations can also cause customer data to leave a chosen residency or boundary area.
For organisations moving from Microsoft 365 Copilot pilots to broader deployment, the implementation detail becomes even more important. Microsoft says EU users of Copilot Chat have EU Data Boundary safeguards, while worldwide traffic may be processed in the EU and other regions depending on capacity. It separately warns that web-search queries sent from Copilot Chat to Bing are not EU Data Boundary-compliant. A blanket approval for “Copilot” is therefore too coarse for a governance programme that has made regional processing or restricted-transfer exposure a material requirement.
UK GDPR asks who receives the data, not only where the server sits
The UK Information Commissioner’s Office has also moved its guidance beyond the simple question of server location. Its updated January 2026 guidance explains that whether an arrangement is a restricted transfer can depend on the legal entity receiving or accessing the personal information, not just the country where the infrastructure sits.
In one example, the ICO says a UK organisation using storage provided by a separate UK company is not automatically making a restricted transfer simply because the servers are outside the UK. Conversely, a provider established outside the UK can raise a restricted-transfer issue even where the servers are physically located in Britain. Where a UK service provider subcontracts processing to an overseas company, the provider itself may be making that transfer.
This is why the data-sovereignty discussion can become muddled when it is reduced to a demand for “UK-hosted” AI. UK hosting may be relevant to resilience, procurement rules, latency, incident response, government-access risk or customer commitments. It is not a substitute for establishing the controller-processor chain, identifying subprocessors, reviewing remote support access, checking the transfer mechanism, and determining what data travels when a model, connector or agent performs its work.
For IT administrators, the relevant inventory is wider than the documents placed in a SharePoint site or the records in an Azure database. It should cover:
- The prompt, completion, grounding data, file attachments, vector-store content and chat history used by an AI application.
- The identity, device, audit, diagnostic and security telemetry generated when users access the service.
- The regions used by dependent services, including storage, Key Vault, Log Analytics, backup, search, networking and model endpoints.
- The legal entity, subprocessors, support arrangements and optional product features that can access or process that data.
- The outbound connectors and agents that can pull information from SaaS applications, internal systems or external web services.
This does not require an organisation to ban public cloud or generative AI. It requires deciding which data and workloads carry a sovereignty requirement, then testing the actual architecture against that requirement. IDC’s own sovereignty analysis makes a similar distinction: the highest-risk workloads are those combining sensitive data, regulatory exposure and critical business processes.
Network visibility is useful, but Expereo has a commercial interest in the answer
Expereo’s CEO Ben Elms frames the findings around network visibility and routing transparency. That focus is reasonable: an enterprise cannot make credible claims about where data moves if it lacks an inventory of routes, egress points, cloud interconnects and third-party dependencies. In a multi-cloud AI environment, the network is often where a regional design becomes a cross-border operating reality.
But readers should recognise the commercial framing. Expereo is a managed network provider, so its conclusion that a sovereignty plan is incomplete without a network strategy naturally aligns with the services it sells. Its sponsored research does not prove that buying a managed network service solves sovereignty. Visibility can reveal a transfer; it cannot by itself establish a lawful transfer mechanism, restrict a model provider’s processing, preserve encryption-key control, or resolve a customer contract that demands in-country support and operations.
The more defensible conclusion is narrower. Network observability belongs in a sovereignty programme because it can validate whether technical controls match policy. It should sit beside data classification, contractual review, identity segmentation, retention controls, encryption and key-management design, audit logging, incident-response procedures and periodic configuration reviews.
What a practical AI sovereignty review looks like
The useful test is whether an organisation can produce evidence for a specific workflow, rather than whether it can point to a provider’s regional marketing page. For a Microsoft-centred environment, that means documenting the tenant’s data-location commitments, identifying which services and licences are actually in scope, and comparing those commitments against the organisation’s own contractual and regulatory requirements.
Azure teams should enforce approved geographies through Azure Policy, review geo-redundant replication and backup choices, and ensure that monitoring workspaces, storage accounts, retrieval indexes and model deployments are aligned to the same regional design. Teams using Azure AI or Azure OpenAI-style services should distinguish regional and global deployment options, then document where inference, prompt storage, content filtering, logging and connected retrieval occur.
Microsoft 365 administrators should review the Data Location Card, the organisation’s regional configuration and the services covered by any data-residency commitment. They should also assess Copilot settings, external access, guest collaboration, connector permissions and Bing-backed web search separately. A policy that prohibits an external AI model from receiving HR or legal data is ineffective if an approved assistant can retrieve that same information through an overbroad connector.
The Expereo-commissioned survey is therefore more useful as a measure of governance anxiety around AI than as a prediction of a rapid wholesale exit from international cloud platforms. The practical response is not to purchase “sovereignty” as a label. It is to make every sensitive AI workflow auditable: what data it uses, where it is processed, who can access it, which transfers occur, and which controls prove that the design still matches the organisation’s stated obligations.