

The advice is not new, and it doesn't need to be. What matters for Windows and Microsoft 365 administrators is that Microsoft's own documentation now sets out a clear order for doing the work. The feature's main argument is that governance has to come before adoption. Below, that argument is separated from the interview opinion and checked against what Microsoft actually documents.
The core problem: old permissions, new speed
The feature opens with a Copilot user asking for everything on a sensitive project and getting documents, emails and chats they were never supposed to see. The concern is real, but it needs one correction. Copilot is not ignoring access controls.
Microsoft states that Microsoft 365 Copilot does not create new permissions or expose data users cannot already access. What it does do is make existing access more discoverable, bringing years of accumulated oversharing, excessive permissions, unlabeled content, unmanaged connectors, and governance gaps into sharper focus. Its security documentation also says overshared or poorly governed content can affect Copilot results and increase risk.
The feature lists familiar causes:
- SharePoint sites shared with whole departments for convenience
- Guest accounts added for one project and never removed
- Folders inheriting access from parents nobody remembers setting up
Microsoft's FastTrack team describes the same mechanism. Content shared with "Everyone," "Everyone except external users," or broad security groups becomes part of Copilot's queryable surface for any licensed user—even if that user would never have manually located those files. Put more bluntly: Copilot makes data once hidden by volume discoverable by intent.
Petri reached a similar conclusion this summer. It argued that the real mistake is treating this as an AI project, because it is really a permissions, ownership, and data lifecycle project that Copilot finally made impossible to ignore.
Section summary: Copilot respects permissions. The risk is that it respects bad ones very efficiently.
The practitioner's view: licensing is not protection
Much of the feature's analysis comes from Saviona Pereira. She is described as a Microsoft-certified Technical Security Architect with more than twelve years of work across Purview, Defender, Sentinel and Entra ID. Her credentials and client observations come only from the interview and could not be independently confirmed. Treat them as one experienced practitioner's view, not survey data.
Her main points:
- The gap is configuration, not procurement. She says most enterprises she works with already own Purview, Defender and Insider Risk Management but treat having the licence as the same thing as being protected.
- Common failure patterns include sensitivity labels that were switched on but never applied to real content, DLP policies left on default settings, and Conditional Access rules written for a much smaller estate.
- AI removes friction. A person searching for data is slow and leaves a trail. An AI assistant uses exactly the access it has been given, at whatever scale the prompt asks for.
- The mess is rarely negligence. In her view, estates simply grew faster than the governance around them, and nobody was given the mandate to go back and fix it.
That last point deserves attention. Many security write-ups quietly blame the admins. This one blames an organizational gap: nobody owns the cleanup.
What Microsoft actually recommends, step by step
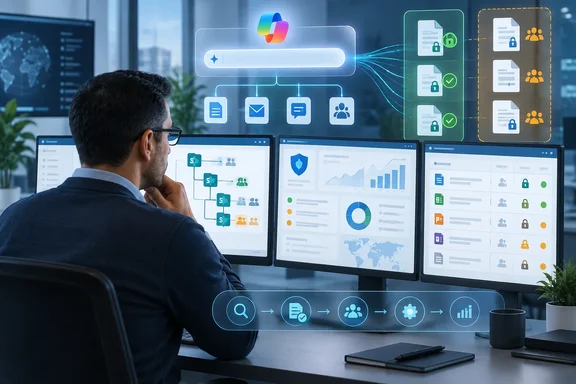
Microsoft's guide to configuring a secure and governed foundation for Copilot turns the "governance first" argument into a concrete procedure. It has three phases: remediate oversharing, set up guardrails, and meet regulatory obligations.
Step 1: Find the high-risk content
- Review Microsoft Purview Data Security Posture Management (DSPM) data risk assessments to identify overshared sites with sensitive data, risky sharing links, and content that is frequently accessed.
- Run the SAM Content Management Assessment to identify sites with oversized audiences, EEEU usage, broken inheritance, inappropriate sharing, and those that are inactive or ownerless. (EEEU is the "Everyone except external users" group.)
Step 2: Apply temporary protections
- Enable SAM Restricted Content Discovery (RCD) to exclude sensitive sites from Copilot discovery. As Petri summarizes it, users retain access, Copilot does not.
- Configure Microsoft Purview Data Loss Prevention (DLP) for Copilot to exclude sensitive content from Copilot grounding.
- Validate through Microsoft Purview Auditing and reports that Copilot no longer surfaces restricted content. This check is how you know the protections worked.
Microsoft describes these as interim controls, to be removed once permissions are fixed. RCD is a tourniquet, not a cure.
Step 3: Fix the permissions
For flagged sites, the guide says to:
- Remove excessive or anonymous access
- Narrow sharing links to approved users or groups
- Start SharePoint Advanced Management site access reviews so site owners can clean up access, down to individual files
- Correct broken permission inheritance
- Assign or confirm an accountable owner for every remediated site
For emergencies, Restricted Access Control empowers admins to lock down a site to a specific set of users, ignoring existing permissions and applying a strict allow list. This gives you a rapid-response option to contain risk while implementing risk remediation measures.
Step 4: Build secure defaults
This is where Pereira's point about agreeing a sensitivity taxonomy with legal and compliance first becomes practical. Microsoft recommends:
- Restricting company-wide sharing groups and "Anyone" links at the tenant level
- Enforcing Restricted Access Control on business-critical sites when they are created
- Requiring site sensitivity labels when sites are provisioned
- Configuring default and automatic sensitivity labeling, so protection doesn't depend on employees remembering to apply labels
On the Copilot side, Purview DLP has two relevant controls:
- Labeled files and emails: You can create a DLP policy to prevent Microsoft 365 Copilot and Copilot Chat from using files and emails that have sensitivity labels when generating responses.
- Sensitive prompts: a prompt-based policy covers sensitive information types such as credit card or passport numbers. It prevents Microsoft 365 Copilot and Copilot Chat from returning a response when prompts contain sensitive data and from using that sensitive data for both internal and external web searches.
One caution: applying a label does not automatically hide content from Copilot. What happens depends on the label, the policy and your configuration. Microsoft notes that user-defined sensitivity label permissions can block Copilot from extracting and interacting with the file content. For example, Copilot agents can't read files that have user-defined sensitivity label permissions. Outside cases like that, DLP policy conditions do the work.
Step 5: Monitor, retain and tidy up
- Use the DSPM Activity Explorer to review Copilot prompts, responses and sensitive-data activity.
- Review Insider Risk Management and DLP alerts.
- Decide how long to keep audit logs and Copilot interactions, based on legal and regulatory needs.
- Use eDiscovery when Copilot-related content has to be searched, preserved or produced.
- Archive or delete stale content. Microsoft notes this also improves Copilot's answers, because the assistant stops reasoning over obsolete files.
Section summary: Assess, contain, fix, set defaults, then monitor. The containment controls are temporary.
Insider risk without treating everyone as a suspect
Pereira argues that insider risk monitoring should be targeted, not blanket. She suggests tying indicators to identity and behavior, such as unusual data movement before someone leaves a role. Microsoft's tooling fits that approach reasonably well, with a few caveats.
- Indicators are off by default. Microsoft's privacy guide says admins must explicitly opt in to indicators such as downloading from OneDrive or sharing SharePoint files externally. Without that opt-in, those activities are not detected.
- Pseudonymization is on by default for analyst and investigator roles, so a user appears as an identifier rather than a name. Microsoft notes that names can still appear in the Insider Risk Management data risk graph, so the anonymity is not complete.
- Role separation means admins who configure policies can't investigate alerts, and investigators can't change policies. Global administrators don't get access to insider risk features by default.
- Departing-user templates such as "Departing user data theft" require the Microsoft 365 HR connector, which imports termination dates and similar data. The scenario Pereira describes depends on HR data being connected.
- Auditing must be on. The Microsoft 365 audit log is a required step. It is on by default but may have been turned off by an administrator.
Microsoft's guide also recommends Insider Risk Management policies that detect inappropriate Copilot usage and automatically move risky users under stricter controls. Like everything else here, that only happens if someone configures it.
AI on the defender's side and the compliance question
The feature also points out that the same machine learning that makes Copilot a potential exposure helps Sentinel and Defender connect signals across identity, email, endpoints and cloud. Pereira's warning is that badly tuned AI in a security operations centre just produces noise faster. Anyone who has faced a wall of untuned alerts will recognize the problem.
Microsoft's newer Security Dashboard for AI, currently in public preview, combines Defender, Entra and Purview signals across Copilot, Copilot Studio agents, Foundry apps and third-party AI tools.
Pereira also says auditors and regulators increasingly want to see controls working, not just written down. That is her professional assessment. It does not point to a specific rule, jurisdiction or effective date. Microsoft's guide does include Purview Compliance Manager assessments against AI-related regulatory requirements, which suggests where the tooling is heading.
Licensing reality check
Before promising leadership a solution, check your agreements:
- Microsoft's foundation guide assumes Microsoft 365 or Office 365 E3/E5, a Copilot licence, and SharePoint Advanced Management, which Microsoft says is included with Copilot licences. It separates foundational E3 capabilities from optimized E5 features.
- According to Consilien's reading of Microsoft's documentation, Restricted Content Discovery requires both a Microsoft Copilot license and SharePoint Advanced Management availability, while Purview DLP for the Copilot location is separate again and depends on your Microsoft 365 security and compliance licensing.
- Insider Risk Management has its own subscription requirements, and some indicators need pay-as-you-go billing.
The verdict
This feature is an interview-driven essay, not breaking news. The quotes come from a single practitioner, and industry-wide claims such as "most organizations leave defaults in place" are anecdotal. Its main argument, though, matches Microsoft's own deployment guide: classify, fix permissions and set defaults before Copilot scales.
For admins, the steps are clear. Run the DSPM and SAM assessments this week. Use Restricted Content Discovery and DLP as temporary containment. Fix permissions with site owners. Enforce labels at provisioning. Scope insider risk policies narrowly and on purpose. Then keep checking that the controls actually work.
Copilot didn't create your oversharing problem. It just made sure somebody would finally notice it.
References
- Securing the data behind the AI: Information protection and insider risk in the Microsoft 365 era - eureporter.co eureporter.co · 2026-09-26T00:00:00+00:00
- Configure a secure and governed foundation for Microsoft Copilot | Microsoft Learn learn.microsoft.com