

Microsoft's September 2026 Security Roundup Promises More on AI Agents Than It Delivers
The roundup is Microsoft's monthly In the Loop post, written by Alym Rayani, vice president of marketing for Microsoft Security. Its introduction says the month's updates help customers "discover and control local AI agents" and extend Zero Trust to agent traffic. The actual list is narrower. Nothing in it is a tool for finding agents running on endpoints. One heading, "Prevent and disrupt threats with Microsoft Defender," has no items under it.
What the post does contain falls into six items across five product lines:
| Product | Change | Stated status |
|---|---|---|
| Defender + Security Copilot | AI email detonation summary for URL and file sandboxing | Available to orgs using both products |
| Purview + Entra Global Secure Access | Network-layer DLP for human and on-behalf-of agent traffic | Generally available |
| Purview auto-labeling | 20M-item / 50,000-site simulations, edit without re-simulating, new reporting | Announced |
| Purview eDiscovery | Search, hold, review, export for user-owned SharePoint Embedded containers | Now supported |
| Purview Data Lifecycle Management | File-level SharePoint archive; Priority Cleanup permanent deletion | Announced |
| Intune | Enterprise App Management, Cloud PKI, Remote Help for GCC High; EAM for DoD | Coming |
The agent theme shows up in one concrete place: the network DLP feature covers on-behalf-of (OBO) traffic, meaning requests an AI agent makes using a user's identity. The Security Copilot summary is the only other AI item, and it's an analyst aid.
Purview Network Data Security on Entra Global Secure Access Reaches General Availability
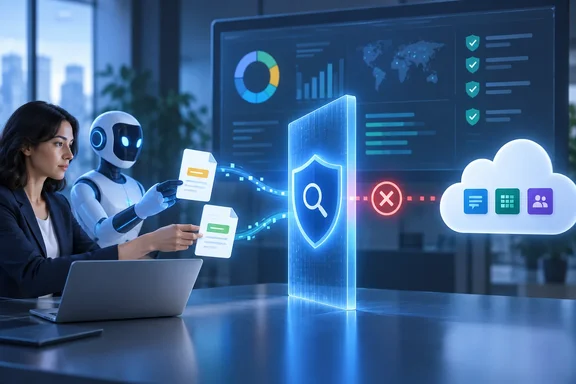
This is the item most tenants will need to decide on. Microsoft says Purview classification and policies are now enforced by Entra at the network layer. That lets organizations spot sensitive files and text in real time and block them before they reach risky destinations. In Microsoft's example, an employee or an OBO agent tries to upload a sensitive document to an unsanctioned AI tool, and the policy stops the transfer before the data leaves.
Microsoft's Purview documentation, last updated September 16, 2026, explains how it works. The network component, here Entra Global Secure Access, watches traffic and sends matching content to Purview for classification and policy evaluation. It uses the same classifiers already set up in other Purview policies. When a DLP policy is enforcing, the exchange between the two services happens in real time. When you only use collection policies for discovery, it runs asynchronously. The documentation lists four monitored activities: text sent to a cloud or AI app, files uploaded, text received and files downloaded. Global Secure Access supports all four, along with both available actions, Audit only and Block.
The scope is broad. Policies can target any app in the Microsoft Defender for Cloud Apps catalog, which holds more than 35,000 apps. They can also use adaptive app scopes that cover whole categories such as generative AI, cloud storage, webmail and social networks. Microsoft's examples include ChatGPT, Gemini and Claude, file uploads to Dropbox, Box and Google Drive, attachments sent through Gmail, and Google Forms submissions.
Licensing is the first hurdle. According to the same documentation, using Global Secure Access requires either Microsoft 365 E7 per-seat licenses, or Purview E5 (or equivalent) per-seat licenses plus Entra Internet Access (or equivalent). Pay-as-you-go billing isn't needed for the Global Secure Access integration. It is needed if you connect third-party SASE or secure-browser products instead, which are billed per network request.
Limits that shape a Global Secure Access DLP rollout
The documentation lists several limits that affect real deployments:
- Purview inspects inline content up to 4 MB for text and files up to 3 MB. The documentation doesn't say what happens to larger payloads, so test that before relying on a block policy.
- Network data security policies don't apply to B2B guest users.
- After setup, policies can take up to 24 hours to reach the network service. Once both services are talking, individual events can take up to 30 minutes to show up in the audit log and activity explorer.
- If the consumer and enterprise versions of an app share a URL, as ChatGPT's do, a policy aimed at the unmanaged app can catch traffic to both.
- Some AI apps, including Runway and Meta AI, sometimes send content in encoded form to dynamically generated endpoints, which can interfere with enforcement.
- The unmanaged-app features apply only to the consumer version of Microsoft Copilot.
Coverage is HTTP and HTTPS across all integrations, and WebSocket support depends on the integration. If a catalog app has more than one entry, as with "QwenAI" and "Qwen Chat," Microsoft advises adding every entry to avoid gaps. If you want a low-risk way to start, Purview's Data Security Posture Management offers a one-click recommended policy called "DSPM for AI - Detect sensitive info shared with AI via network." It detects without blocking, and you can edit it like any other collection policy.
Security Copilot's Email Detonation Summary Explains Sandbox Verdicts
For tenants licensed for both Microsoft Defender and Microsoft Security Copilot, Microsoft is adding an AI-generated email detonation summary. Detonation means running a URL or attachment in a sandbox and watching what it does. The summary explains in plain language the results of the URL and file sandboxing. The goal is to cut the manual work of connecting detonation evidence with other signals during investigation and hunting.
Analysts already have the raw material. In Defender for Office 365, the Email entity page records which detection technology fired, including "File detonation," where Safe Attachments caught a malicious attachment, and "URL detonation," where Safe Links caught a malicious URL. It also shows attachment and URL views with threat verdicts, malware families and SHA256 hashes. The new summary sits on top of that evidence and interprets it. It doesn't replace it. Microsoft gives no numbers for time saved and no rollout schedule beyond including the feature in this roundup. Because it depends on having both products, most Microsoft 365 E5 tenants without Security Copilot won't see it.
Purview Auto-Labeling Scales Simulations to 20 Million Items
Auto-labeling applies sensitivity labels to content that matches policy conditions. Microsoft now says simulations can cover up to 20 million items and up to 50,000 sites through adaptive scopes. Administrators can also edit a policy without re-running the simulation. New audit insights and reports show policy coverage and processing activity.
The edit change solves a real pain point. In simulation mode, a policy shows which items it would label without changing anything. Microsoft's current guidance on reviewing results tells admins who get too many false positives, or too few matches, to edit the conditions and restart the simulation. That means another full scan for every tweak. Skipping that loop makes tuning faster. The roundup doesn't explain how edited policies get validated without a fresh simulation, so be cautious before enforcing a policy whose conditions changed after its last simulation. The same guidance also warns that simulated match counts are estimates drawn from sampled content, and actual enforcement counts can differ.
This follows last month's throughput increase. Microsoft's August roundup said auto-labeling policies in Microsoft Purview now process up to 500,000 SharePoint and OneDrive files per day, up from 100,000. Taken together, the two months raise both how much you can test and how much gets labeled, which suits large tenants preparing content for Microsoft 365 Copilot.
Purview eDiscovery Reaches Copilot Pages and Loop in SharePoint Embedded Containers
Content from Copilot and Loop has been awkward for legal teams. Copilot Pages, Copilot Notebooks and Loop "My workspace" content live in user-owned SharePoint Embedded containers. Microsoft's Loop documentation says these containers have no standalone interface and no ordinary user-assigned site URL. In admin tools they may appear under the Loop application. The documentation also warns that selecting a user's OneDrive in an eDiscovery case doesn't include those Pages or Notebooks. The container has to be added as a separate data source.
With the September change, Purview eDiscovery supports search, hold, review and export for these user-owned containers. Microsoft says investigators can find content mapped to a user without asking a SharePoint administrator for the container URL. That covers Loop, Copilot Pages, Copilot Notebooks, and app content such as Outlook newsletters. An optional HTML conversion makes a more readable copy for downstream legal review tools.
The practical gain is a smaller team and fewer handoffs. An eDiscovery manager can now preserve a custodian's Copilot-created work without first opening a ticket with SharePoint admins. For organizations where holds have to go in quickly after litigation is anticipated, that cuts a real delay.
Purview Data Lifecycle Management Splits Archiving From Permanent Deletion
Two lifecycle features arrive together, and they do opposite things.
The first lets administrators archive inactive SharePoint content without archiving the whole site. Archived content stays subject to retention and legal hold policies and stays discoverable in eDiscovery. It drops out of Microsoft 365 Copilot indexing until someone reactivates it. Microsoft's retention documentation adds one operational detail: a reactivated file can't be archived again until a 120-day cooldown has passed.
The second, Priority Cleanup, permanently deletes approved content. Microsoft names stale Teams recordings and transcripts as examples. Once deleted, the content no longer appears in eDiscovery, SharePoint search or Microsoft 365 Copilot. Microsoft's documentation says the permanent-deletion option skips the SharePoint and OneDrive recycle bins and runs only after the required review and approval. That same documentation describes a preview rollout that began August 24, 2026. The September post doesn't say Priority Cleanup is generally available, so assume it's still in preview until your tenant shows otherwise.
For Copilot governance, the choice is simple. Archive when you want Copilot to stop reading content you still have to keep. Use Priority Cleanup only when you're sure nothing obliges you to keep it. Priority Cleanup deletions can't be recovered from the recycle bin, so check them against active holds and retention schedules before approving.
Intune Enterprise App Management, Cloud PKI and Remote Help Head to GCC High
Microsoft says three Intune capabilities are "coming" to Government Community Cloud High (GCC High): Enterprise Application Management, Microsoft Cloud PKI and Intune Remote Help. Enterprise Application Management is also being offered to Department of Defense (DoD) organizations. The stated benefits are simpler application management, modern certificate lifecycle management and faster device troubleshooting, all inside accredited cloud environments.
The post gives no dates. Microsoft's own Intune documentation muddies things further: its government service description, updated in June 2026, already lists Cloud PKI and Remote Help among GCC High and DoD capabilities, and the Enterprise Application Management page lists GCC High and DoD as supported clouds. Until Microsoft clarifies, government tenants should check what's actually enabled in their own admin center. Don't plan migrations around either the announcement or the documentation alone.
What this means for you
Purview and Entra administrators have the most to act on this month. Everyone else mostly needs to check eligibility and tenant status.
- Confirm licensing before scoping Global Secure Access DLP: Microsoft 365 E7, or Purview E5 plus Entra Internet Access. Start with the DSPM for AI detection policy before turning on Block.
- Plan around the 3 MB file and 4 MB text inspection limits, the missing coverage for B2B guests, and up to 24 hours for policies to reach Global Secure Access.
- Tuning auto-labeling policies should be faster now. Still review a policy's results again after significant condition changes, because simulation counts are sampled estimates.
- Legal and compliance teams should update eDiscovery playbooks so Copilot Pages, Copilot Notebooks and Loop containers are added as their own data sources rather than assumed to come in with OneDrive.
- Use file-level archiving to pull stale SharePoint content out of Copilot's reach while keeping holds intact. Treat Priority Cleanup as irreversible, recycle bin included.
- GCC High and DoD tenants should check actual availability of Enterprise App Management, Cloud PKI and Remote Help in their admin center, since Microsoft's announcement and documentation disagree.
September's roundup is mostly about data governance for the Copilot era. Its most important change is that Purview DLP now sits in the network path, where it can stop an AI agent's upload the same way it stops a user's. Tenants with the licenses can start in audit mode today. Microsoft is pointing to Ignite, November 17–20, 2026, in San Francisco and online, as the next big showcase for its security products, so expect more agent-focused controls there.