

Barracuda AI Data Security moves from tracking tools to inspecting data
Barracuda already offered controls for discovering and governing AI use. Its Q1 2026 announcement described visibility into shadow AI—tools employees use without organizational approval—along with risk scoring and policies to block or redirect noncompliant use. SiliconANGLE’s March 24 reporting described that capability as an addition to BarracudaONE at no additional cost.
The September announcement moves the enforcement decision closer to the information being shared. Knowing that an employee uses a chatbot answers an application-governance question. Inspecting the prompt or uploaded file lets an administrator make a more specific decision: whether that interaction contains information the business has decided must stay out of the service.
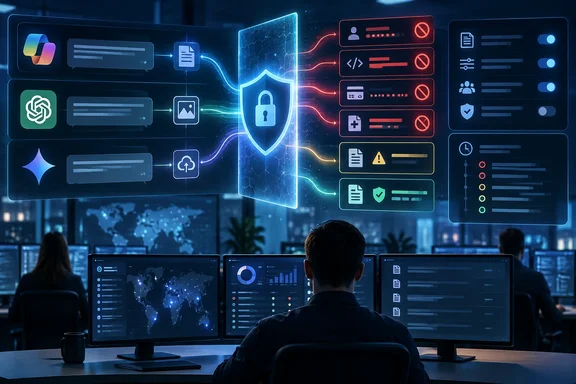
Barracuda’s product page says AI Data Security inspects prompts and file uploads in real time and can block, warn about or redact sensitive content before it reaches an AI service. Its prebuilt detection categories include personal information, credentials, source code, payment data and health records. Detection is powered by Barracuda IQ, with management through BarracudaONE.
That creates a useful distinction between approving a tool and approving every use of it. An organization can permit an AI service while placing restrictions on the data employees submit. Barracuda describes policies that vary by AI tool, team and data type, allowing a business to express those decisions without making every chatbot an all-or-nothing choice.
Barracuda lists coverage across more than 1,300 generative AI tools, including Copilot, ChatGPT, Claude and Gemini, in its Premium offering. That is a vendor coverage claim, not a measurement of detection accuracy. The material available at launch describes the controls and intended workflows but supplies no independent accuracy or performance results.
Default blocking makes policy review part of deployment
Barracuda says high-risk categories are protected by default, and SiliconANGLE reports that sensitive-data blocking is active from deployment. The product page also describes a visibility-first path in which customers discover AI use before adding enforcement. Those statements describe different stages of adoption: starting with discovery is separate from enabling an inspection product whose default policies already take action.
For administrators, default blocking is an operational choice, even when it arrives as a preconfigured setting. Before enabling enforcement for a department, the team needs to understand which data categories trigger intervention and whether the intended response is a block, warning or redaction. Barracuda’s promise of minimal initial tuning does not decide which disclosures a particular business should permit.
The three responses have different practical consequences. A block prevents the flagged submission from proceeding; a warning alerts the user; redaction removes identified content. Barracuda does not specify the exact user experience for every supported service in the available material, so administrators should establish how their chosen action behaves in the applications employees actually use.
The company’s examples illustrate the intended policy granularity: engineering can use an AI coding assistant, sales can be restricted from pasting customer data, and marketing can receive a warning about campaign details. These are examples of configurable business policy, not a requirement to organize departments that way. Their value is showing that permission to use an application and permission to send a category of information can be separate decisions.
SiliconANGLE describes firewall-style rule screens and assistance from Barracuda’s Bailey assistant when writing custom rules. Barracuda’s product page confirms familiar policy workflows and AI-assisted setup. For a small IT team, the attraction is reducing the work needed to translate an acceptable-use policy into enforcement; deciding the acceptable use still belongs to the organization.
Copilot support needs a narrower reading than “Microsoft 365 protection”
Microsoft Copilot is explicitly among the named services, making the launch relevant to Microsoft-focused IT teams as well as organizations using several vendors’ chatbots. However, the product material names Copilot without establishing a complete matrix of Copilot editions, interfaces or workflows. Administrators should keep that boundary visible when assessing coverage.
Barracuda describes an access-and-inspection approach. For existing SecureEdge Access customers, its product page says the service uses existing web inspection to identify AI traffic where SecureEdge Access is enabled, applies user and group policies, and adds AI-specific inspection. The company says those customers can extend their protection without a separate deployment project.
The phrase “where SecureEdge Access is enabled” is important. The supported claim concerns traffic reached by Barracuda’s inspection controls. It should not be expanded into a promise that every AI interaction on every corporate or personal device is automatically covered.
Barracuda’s SecureEdge documentation explains why the access plan also matters. DNS Access concentrates on DNS-based filtering and visibility. Internet Access adds a secure web gateway and inspection of encrypted web traffic. Premium Access combines those capabilities with private-resource access and lists data loss prevention. Discovering that a device contacted an AI service and inspecting the contents of an upload require different levels of visibility.
For a Microsoft 365 administrator, this positions AI Data Security as a control over inspected interactions with AI services. The available documentation does not establish integration with Microsoft 365 tenant permissions, sensitivity labels or Copilot-specific internal data access. Assess it against the submission-control problem Barracuda describes, while retaining separate governance decisions about which business information users and applications may access.
Before treating Copilot as covered in a deployment plan, ask Barracuda to identify the supported Copilot experience, client and traffic path. That is more useful than relying on the product name alone, particularly where employees use multiple interfaces to reach AI tools.
AI detection and audit exports serve different security decisions
Barracuda’s claims extend beyond sensitive-data detection. Its product page says the service inspects information sent to AI tools and content returned by them, looking for prompt-injection attempts, jailbreaks and policy violations. SiliconANGLE also reports screening for hate speech and employer-defined prohibited topics.
In broad terms, prompt injection concerns instructions that try to redirect an AI system’s behavior, while jailbreaks seek to bypass its restrictions. Barracuda says its detection combines machine-learning models with pattern matching and aligns with the Open Web Application Security Project’s Top 10 for large language model applications. That describes the vendor’s detection approach and risk framework; it is not a certification that every listed risk is eliminated.
These controls serve a different decision from identifying a password or customer record in an upload. Data-loss prevention asks whether protected information is being disclosed. Interaction screening asks whether the exchange contains instructions or content that violate security or acceptable-use policies. Both can be useful, but buyers should evaluate the specific capability they need instead of treating “AI security” as one indivisible feature.
The audit trail is more concretely described. Barracuda says every inspection and action is logged with the user, applicable policy, detection type, action taken and timestamp. One-click exports are intended to support internal reviews, compliance checks and insurance questionnaires. Those fields can help explain which policy intervened and what the service did.
An enforcement record is useful evidence of a control operating. Its value for an audit still depends on the scope of inspected activity and how long the relevant records remain available. Barracuda’s description of logged fields does not establish that complete prompts and uploaded files are retained, so customers should distinguish an event trail from a full interaction archive.
SecureEdge’s access-plan documentation lists reporting for 30 days, but it does not clearly establish that the new AI-specific audit records share that exact retention window. Organizations with evidence-retention requirements should settle the AI log retention and export arrangements before relying on the feature for an audit or insurance submission.
October availability leaves an important licensing distinction to resolve
SiliconANGLE reports that AI Data Security becomes available in October 2026 and will be included at no additional cost in Barracuda SecureEdge Premium Access. That is a specific subscription entitlement, not a statement that the new enforcement capabilities are free for every BarracudaONE customer.
Barracuda’s product page separately presents three AI Data Security plans. Foundation is free and provides shadow-AI and AI data-security risk discovery. Premium lists data protection across more than 1,300 AI tools. Premium Plus describes real-time prompt inspection and data-loss prevention across AI tools and workflows. Pricing for Premium and Premium Plus is available on request.
The overview does not fully reconcile those AI Data Security tiers with the reported SecureEdge Premium Access bundle. In particular, customers should establish which inspection, redaction and workflow capabilities their existing entitlement includes. Similar plan names are not enough to infer identical feature sets.
There is also a timing distinction in Barracuda’s documentation. The SecureEdge access-plan matrix marks its general data-loss-prevention capability as scheduled for September 2026, while SiliconANGLE gives October availability for AI Data Security. Those are differently scoped descriptions; the September entry should not be used to declare the newly announced product generally available today.
For managed service providers, SiliconANGLE reports multitenant management across customer accounts and pricing that can be bundled into existing service packages. That could make the controls easier to offer as part of an ongoing managed service. Each customer’s permitted tools, protected information and reporting requirements would still need to be reflected in its own policies.
Evaluate Barracuda AI Data Security against the workflows you need to control
Existing SecureEdge Premium Access customers have the clearest reason to investigate the October release first: the reported bundle could extend infrastructure they already operate. Other buyers should begin with the AI submissions they need to control and establish the subscription and inspection requirements from there.
The most useful preparation is a scoped evaluation plan, not an assumption that all 1,300-plus listed tools behave identically. The available evidence supports the following checks:
- Confirm the October availability date and the exact AI Data Security features included in your SecureEdge or standalone subscription.
- Identify the Copilot, ChatGPT, Gemini or other AI interfaces employees actually use, and obtain confirmation that those interactions pass through supported inspection.
- Review the default protected categories and decide where blocking, warnings or redaction match your organization’s approved data-sharing rules.
- Evaluate the advertised controls with representative, non-sensitive test material before applying consequential blocking policies broadly.
- Establish the AI audit log’s fields, retention and export arrangements against your reporting obligations.
- For an MSP deployment, map policies and reporting requirements to each customer account rather than assuming one shared policy fits every organization.
Barracuda’s concrete step is to give administrators control over information submitted to AI services, alongside the controls they already use to discover or restrict those services. October availability will make the relevant decision a deployment and entitlement question: whether the covered workflows, policy actions and audit evidence match the organization’s actual AI use. That is the standard on which this release deserves to be evaluated.