

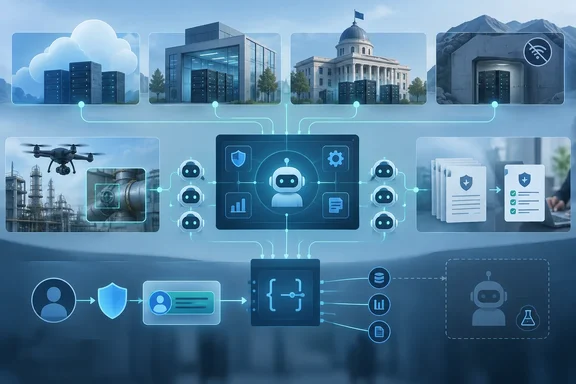
DataRobot's Agent Workforce Platform targets the environments hyperscalers leave behind
Futurum analyst Nick Patience writes that DataRobot sorts the agentic AI market into three tiers. The first is copilots such as ChatGPT and Microsoft Copilot. The second is agents that live inside one application, such as Salesforce Agentforce or Workday. The third is what DataRobot calls agent workforce agents, which work across data and processes throughout an enterprise. DataRobot openly leaves single-cloud, hyperscaler-native deployments to AWS, Azure and Google. It is aiming at the harder environments: multi-cloud, hybrid, on-premises, sovereign and air-gapped.
DataRobot's documentation supports the deployment side of that claim. It describes the platform as one place to build, operate and govern predictive models, generative AI and agents. The listed deployment options are managed SaaS, virtual private cloud and self-managed infrastructure, which includes on-premises, private GPU clouds, sovereign GPU clouds, air-gapped sites and the major public clouds. DataRobot also says the platform is co-engineered with NVIDIA and validated on infrastructure from Dell and Nebius. That validation claim is DataRobot's own. It does not mean every capability works identically in every environment.
The product dates to July 31, 2025, when DataRobot announced the Agent Workforce Platform as co-engineered with NVIDIA and named support for agent frameworks including CrewAI, LangGraph and LlamaIndex. The infrastructure partnerships came later. A Nebius "AI Factory for Enterprises" offering is dated March 18, 2026, and a pre-validated blueprint for Dell AI Factory with NVIDIA is dated May 18, 2026. The documentation also covers agents built elsewhere. Teams can bring agents built with third-party frameworks into DataRobot's Registry, which tracks versions and generates compliance documentation. Console then monitors deployed agents and traces their decisions and tool calls.
Patience considers the gap DataRobot is aiming at to be real. He also calls it "a narrow definition of victory." DataRobot is not trying to beat Agentforce inside Salesforce or Azure inside a single-cloud Azure customer. Its bet is that the rest of the market stays underserved long enough for DataRobot to build a business there.
The Chevron Safe Start agent shows the edge use case
The Chevron deal is the most concrete evidence for the strategy. DataRobot announced on June 2, 2026 that it is collaborating with Chevron U.S.A. Inc., a subsidiary of Chevron Corporation (NYSE: CVX), to apply agentic artificial intelligence at the edge to assist autonomous inspection operations at Chevron facilities. The work supports Chevron's Facilities and Operations of the Future initiative.
Before this, Chevron uses aerial and terrestrial robots worldwide to inspect and monitor equipment for abnormal conditions. Traditionally, each robotic mission requires operator verification of operating conditions through a permitting process, adding time and additional steps before work can begin. Under the new setup, a Safe Start agentic assessment runs inside the DataRobot platform using NVIDIA NIM microservices. It checks operating conditions before and during each mission, and the system leverages existing hard-wired gas sensors, supplemental vision systems and AI models to assess conditions locally at the asset. The practical change is that a one-time approval gate becomes continuous monitoring while work is underway.
Chevron's program manager for the initiative, Cari Armpriester, described the benefit as "reducing reliance on manual, point-in-time checks and validating conditions continuously while work is underway." Neither company has published measured safety, cost or productivity results. Reduced exposure and more efficient robotics deployment are stated goals, not reported outcomes.
Futurum gives a more detailed NVIDIA component list than the press release. It names Nemotron for reading sensor data, PhysicsNeMo for physics-based gas-plume simulation, NIM for the safety-assessment layer, NeMo for guardrails and evaluation, and cuOpt for drone routing. The official announcement confirms only NIM. DataRobot's own marketing supports the plume and routing features: its LinkedIn account says Chevron's agents handle inspections by routing drones through gas-free corridors, predicting gas plumes in real time, and keeping operators in the loop via natural language chat. Those are vendor descriptions, not an independent technical review.
Aon's onboarding agents are still at the exploration stage
The Aon deal is less far along than the Chevron one. On January 26, 2026, Aon announced a collaboration with DataRobot "that will explore ways" to improve client onboarding and servicing with agentic AI. Aon said it intends to use DataRobot's autonomous, reasoning-based agents in selected parts of the insurance lifecycle, with Aon staff still overseeing and validating the work.
The two workflows are specific. For onboarding, the aim is to consolidate historic documents, policy binders and policy information to speed up new placements and renewals. For servicing, the focus is certificate generation, invoice processing and automatic ID card issuance. Aon said clients have tested components of these AI-enabled features for more than a year. The announcement gives no figures, and it does not say that all of these agent workflows are in general production.
This fits the kind of document-heavy back-office work that DataRobot's governance model is built around. The release describes it as a collaboration, and Aon uses words like "intends" and "aims." Readers should treat Aon as a large enterprise committing to a pilot-to-production path, not as a finished deployment.
DataRobot's three governance layers
Futurum describes the stack as a Build layer and an Operate layer, with three governance disciplines underneath. DataRobot's documentation lists the same three:
| Governance layer | What DataRobot says it covers |
|---|---|
| AI and agentic governance | Approval workflows and versioning before an agent ships, plus real-time production moderation for bias, hallucinations, prompt injection and leakage of personal information |
| IT governance | Agent-specific identity and entitlements, with consistent lineage across agents, tools and applications |
| Infrastructure governance | Gateways, fair-use policies and cost controls to keep GPU spend predictable |
Futurum's version of the AI governance layer also includes drift, correctness and tool-calling accuracy, and it places GPU cost and utilization under infrastructure governance. These describe what the platform is meant to do. They say nothing about which controls a particular customer has switched on.
Futurum also reports that DataRobot is splitting its control plane from its data plane. The goal is for the CPU-heavy governance and orchestration layer to run separately from a GPU-heavy inference cluster such as an NVIDIA SuperPod. This is on the roadmap, not shipping. If it arrives, sites with limited GPU capacity could keep inference on dedicated hardware while governance runs on ordinary servers.
Two different Entra ID stories
Futurum says DataRobot's agent-identity integration with Okta is live, while a comparable Microsoft Entra ID integration is in proof of concept and targeted for general availability "within the next few months." Patience argues this shows the agentic identity layer is less mature than DataRobot's marketing suggests. For a platform whose pitch is running wherever a customer's identity systems already are, missing Entra support would be a real gap.
Admins should know that DataRobot's current documentation already names Microsoft Entra ID, along with Okta, Ping and Auth0, as a supported identity provider for inbound OAuth. Inbound OAuth lets callers authenticate to the DataRobot API with access tokens from the organization's own identity provider (IdP) instead of DataRobot-issued API keys. The documentation says this feature is separate from outbound OAuth, where DataRobot authenticates to third-party services for you. The two claims can both be true. Entra-based API sign-in is documented now. The agent-identity integration Futurum describes is a different function, and it has no public GA date.
Inbound OAuth works through a token exchange based on OAuth 2.0 (RFC 8693). A user signs in to Entra ID and gets an access token. The client sends that token to DataRobot's token-exchange endpoint. DataRobot checks the token against the IdP's published signing keys (the JWKS URI), confirms it carries the required dr.impersonation scope and the correct audience, and maps the user to a DataRobot account. DataRobot then issues its own short-lived access token for API calls. The IdP remains the source of truth for identity, and groups in the token can map to DataRobot groups that control which agents a user can reach.
Prerequisites before an Entra ID rollout
- SAML single sign-on must already be enabled for the DataRobot organization, or enhanced global SAML SSO for the cluster. Inbound OAuth is not available to organizations that sign users in only through LDAP or DataRobot usernames and passwords.
- DataRobot must enable inbound OAuth for the organization. It needs no extra license but is off by default, so customers have to ask their DataRobot representative.
- The admin needs the Organization Administrator or System Administrator role.
- On the Self-Managed AI Platform, exactly one of two cluster settings must be enabled:
ENABLE_GLOBAL_EXTERNAL_APPLICATION_AUTHENTICATIONorENABLE_ORGANIZATION_EXTERNAL_APPLICATION_AUTHENTICATION. Only one configuration scope can be active at a time, and it must match the SSO scope.
Documented Entra ID configuration steps
- In DataRobot, open Admin settings > External Application and copy the Audience value from OAuth Details. It looks like the DataRobot host followed by the organization ID.
- In the Microsoft Entra admin center, go to App registrations > New registration and create an app to represent DataRobot. Under Expose an API, set the Application ID URI to that exact audience value. A custom identifier URI like this requires the v2.0 access-token format.
- Still under Expose an API, add a scope named
dr.impersonation. - Open the tenant's OpenID configuration document for the v2.0 endpoint. Enter its
issuervalue as the External issuer in DataRobot and itsjwks_urivalue as the External JWKS URI. The issuer must match the token version the app issues. - In the client app registration your users sign in with, go to API permissions, add the
dr.impersonationscope, grant admin consent, and assign the users who need API access. - Map the claims in DataRobot. Entra puts scopes in
scpand the username inpreferred_username(orupn). For group mapping, add the groups claim under the app's Token configuration.
The documentation also lists the failure modes. A token without the dr.impersonation scope is refused access, and a token whose audience does not match is rejected as invalid_target. Optional just-in-time provisioning creates a DataRobot account the first time a valid token arrives for an unknown user. If no non-builder seat is free, the account is still created, just without a seat. The same configuration can be managed through the /api/v2/externalApplicationConfigurations/ endpoint for infrastructure-as-code setups.
Where Futurum sees DataRobot's advantage wearing thin
Patience accepts two of DataRobot's three claimed differentiators: deep vertical expertise and co-engineering with NVIDIA and Dell. He calls the third, freedom from lock-in to any one model, cloud or orchestration layer, "a bit of a stretch." His reasoning is that the most detailed production deployment, Chevron, runs almost entirely on NVIDIA software. The platform avoids tying customers to one hyperscaler but is heavily committed to one silicon and software vendor.
His view of go-to-market is similar. DataRobot combines an AI Factory channel, with pre-installation deals through NVIDIA Cloud Partners such as Dell and Nebius, and a business-application channel built on SAP endorsement and a Genpact partnership. Futurum says a well-funded competitor could copy both by signing similar deals and hiring similar vertical specialists.
Futurum also reports that DataRobot says its platform-to-Center-of-Excellence (services) revenue split is close to 80/20, with a target of 75/25. By Futurum's reading, large wins such as Chevron and Aon depended on heavy forward-deployed engineering. No other outlet has reported that ratio.
Adoption data points the same way. Futurum cites ETR's July 2026 TSIS survey, which gave DataRobot a Net Score of 16 and Pervasion of 4% from 49 citations. Futurum itself calls that sample small and the figures directional. In ETR's March 2026 AI Product Series survey of 467 respondents, about 5% said they use DataRobot and plan to continue, and 73% said they have no plans to evaluate it. Outside the named accounts, DataRobot is not widely known among enterprise buyers.
What this means for you
Organizations that run AI across on-premises, sovereign or air-gapped estates should put DataRobot on their evaluation list. Microsoft-centric shops should check exactly which identity feature they need before committing.
- If you need Entra ID sign-in for API calls to DataRobot, it is documented today through inbound OAuth, but only with SAML SSO in place and after DataRobot enables the feature.
- If you need Entra-native identities for the agents themselves, Futurum reports that integration is still in proof of concept, so ask DataRobot for a dated GA commitment rather than relying on "the next few months."
- Treat the Chevron and Aon results as vendor-stated goals, since neither company has published measured safety, cost or productivity figures.
- Budget for services. Futurum's reporting suggests large production wins came with substantial DataRobot engineering support, not the platform alone.
- If avoiding lock-in is a priority, note that the flagship Chevron stack depends heavily on NVIDIA NIM and related NVIDIA software, even though it is not tied to one cloud.
DataRobot's case is strongest where it has chosen to compete: governed agents in places Azure, AWS and Google Cloud reach only partly. The Chevron and Aon announcements, the published governance model and the working Entra ID token exchange show real substance. Futurum points to three near-term signals: GA of the Entra agent-identity integration, the control-plane and data-plane split, and progress toward the 75/25 services ratio. Together they will show whether DataRobot is building a product advantage or relying on being early and well partnered.