

Agentic Autofix Starts Writing Security Fix Patterns Into Copilot Memory
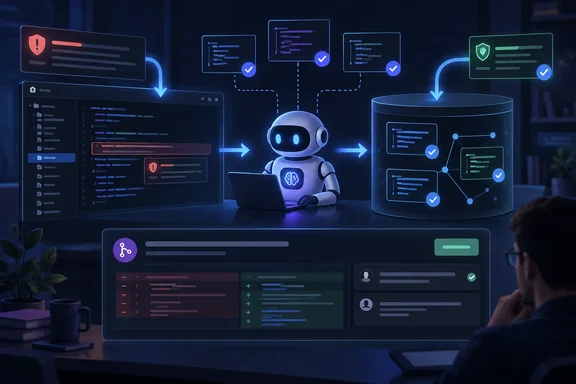
GitHub's changelog entry is short, and it describes a two-way connection. When a developer uses agentic autofix, it looks through existing memories for context that could help resolve the security alert. When it produces a fix, it stores that fix pattern as a memory. GitHub says these memories can help agentic autofix resolve more alerts. They can also teach other Copilot features, with Copilot code review and Copilot cloud agent named as examples, about the secure development patterns specific to a repository.
The entry names one condition: the behaviour applies only to customers who have enabled Copilot Memory. GitHub's Memory documentation states the rule directly: memories are only created and used by Copilot when Copilot Memory has been enabled for the user initiating the Copilot operation. In practice, the developer who assigns an alert to the agent decides whether memory is involved in that run. The repository's settings do not decide it.
The changelog leaves several things out. It doesn't say which alert types or languages benefit most, it gives no rollout schedule or settings path specific to this change, and it makes no claim about better fix quality or speed. It says memories can help, which is a smaller claim than "will improve."
How Agentic Autofix Works Before Memory Enters the Picture
Agentic autofix is itself recent. According to a hands-on write-up by Microsoft MVP Marcel Lupo on DEV Community, GitHub announced agentic autofix for code scanning alerts in public preview on 10 July 2026. The workflow in that account runs like this. You assign one or more code scanning alerts to Copilot. Copilot cloud agent inspects relevant files across the codebase. It proposes a fix and attempts to validate it. It iterates when necessary. It opens a draft pull request containing the changes, an explanation, and validation details.
The same write-up notes that a July 16 editor's note from GitHub clarified that assignment works for all first-party and third-party code scanning alerts. In other words, eligibility is not limited to CodeQL findings. Alerts uploaded by integrated tools through SARIF can also be assigned. The author also describes agentic autofix as a paid public preview.
Memory therefore fits into an existing loop: an alert comes in, the cloud agent investigates, and a draft pull request goes out. Memory adds a step before the investigation, where the agent pulls in repository context, and a step after the fix, where it records the pattern. The output is still a draft pull request, so a human still decides what merges. The announcement doesn't change that.
Why Copilot Memory Turns One Fix Into Shared Knowledge
Copilot Memory launched on January 15, 2026. GitHub then described it as a system in which Copilot automatically captures tightly scoped insights called "memories" as it works in your repositories. The launch changelog listed three properties. Memories are repository-specific and validated against the current codebase before use. Shared across Copilot features, so what coding agent learns can help code review. Automatically expired after 28 days to prevent stale information.
Sharing across features is the key to understanding this week's change. GitHub's documentation says facts and preferences captured by one Copilot feature can be used by another. For example, if Copilot cloud agent discovers how your repository handles database connections, Copilot code review can later apply that knowledge to spot inconsistent patterns in a pull request. Similarly, if Copilot code review learns that certain settings must stay synchronized across two files, Copilot cloud agent will know to update both files when changing one.
Security was part of the plan from the beginning. In the January engineering post, GitHub principal machine learning engineer Tiferet Gazit wrote that the goal was to evolve GitHub Copilot into an ecosystem of agents that collaborate across the entire development lifecycle from coding and code review to security, debugging, deployment, and maintenance. The post's first cross-agent example was about security. A coding agent that learns how a repository handles database connections while fixing a vulnerability passes that knowledge to code review.
Agentic autofix now contributes to that shared pool directly. Suppose it learns that a repository sanitises input through a particular internal helper, or wraps queries in a specific way. That pattern can come up again when code review looks at a new pull request touching similar code. This is our inference from GitHub's stated design, and GitHub hasn't published an autofix-specific example. The value is highest in codebases with local security conventions that a general-purpose model wouldn't know.
The documentation available when we checked lists Copilot cloud agent, Copilot code review, and Copilot CLI as Memory's current users. This week's changelog adds agentic autofix to that set. The docs also separate how each feature uses Memory: Copilot CLI applies repository-level facts and the user-level preferences of the user who initiated the operation. Copilot code review uses repository-level facts only. The changelog doesn't say whether agentic autofix reads personal preferences. Its wording, "secure development patterns unique to your repository", points to repository-level facts.
Citation Checks Keep Stale Security Memories in Check
A memory system that stores security fixes raises an obvious risk. A pattern from an abandoned branch, or a deliberately planted "fact", could steer a later fix the wrong way. GitHub's answer is a technique it calls just-in-time verification. The documentation explains that each memory that Copilot generates is stored with citations. These are references to specific code locations that support the memory. When Copilot finds a memory that relates to the work it is doing, it checks the citations against the current codebase to validate that the information is still accurate and is relevant to the current branch. The memory is only used if it is successfully validated.
The engineering post adds how retrieval works. When an agent starts a new session, we retrieve the most recent memories for the target repository and include them in the prompt. Then, before applying any memory, the agent is prompted to verify its accuracy and relevance by checking the cited code locations. If the code contradicts the memory, or if the citations are invalid (e.g. point to nonexistent locations), the agent is encouraged to store a corrected version of the memory reflecting the new evidence.
The verification is a model-driven check. The agent is "prompted" and "encouraged" to verify, so this isn't a deterministic gate. GitHub reported in January that when it seeded test repositories with adversarial memories, agents consistently spotted the contradictions and corrected the memories. That test covered the agents using Memory at the time. GitHub hasn't published a comparable evaluation for agentic autofix.
The same limit applies to GitHub's headline numbers. In January it reported A/B results of a 7% higher pull-request merge rate for the coding agent (90% with memories against 83% without) and 2% more positive feedback on code-review comments (77% against 75%). Those are GitHub's own measurements of other agents. They say nothing yet about whether memory-assisted security fixes are more accurate.
Who Controls Copilot Memory for Agentic Autofix in Business and Enterprise Tenants
Memory is enabled per user, not per repository, and the default depends on how Copilot is licensed. The January launch notes split it this way. Individual users (Copilot Pro or Pro+): Enable Copilot memory in your personal Copilot settings. Organizations and enterprises: Enable through policy settings in your organization or enterprise settings. GitHub's current documentation goes further. Memory is on by default for individual plans. For organisation- and enterprise-managed plans, an administrator has to enable the policy first, and individual users can then opt out. The documentation also limits Memory to paid Copilot plans during the preview.
For admins, this means agentic autofix only uses Memory in an organisation that has already allowed Memory by policy, and even then only for developers who haven't opted out. No tenant-wide switch arrived with this changelog. Admins should still read a September 24 changelog titled "Default Enablement of Copilot features for Copilot Business and Enterprise." That entry is separate from this one, and it's worth checking whether it changes your organisation's Memory defaults.
Permissions follow repository access. GitHub's engineering post states that memories for a given repository can only be created by actions of contributors with write permission in that repository, and can only be used in tasks on that same repository started by users with read access. A security fix pattern learned in one repository does not travel to another. GitHub's documentation adds that repository owners can review and manually delete stored facts. Users can view and delete their own preferences, and on Copilot Business and Enterprise, administrators can view, export or delete user preferences in bulk or per user. Third-party guides from consultancies such as Arinco point repository owners to Repository Settings > Copilot > Memory to manage stored memories. That path comes from a February 2026 guide, so confirm it against your current GitHub interface.
Retention is short by design. Unused memories expire after 28 days. When Copilot validates and uses an entry, the timer can reset, so a fix pattern that keeps proving relevant will stay, while one tied to since-deleted code will lapse.
What this means for you
If your organisation is piloting agentic autofix and already allows Copilot Memory, you have nothing to switch on. Your next security fixes will start adding to the repository's memory store, and your job is to watch what gets stored. If Memory is off by policy, this change does nothing for you. Deciding to turn it on now means accepting that security fix patterns will be shared with code review and cloud agent in that repository.
Security teams should keep reviewing agentic autofix output the same way as before. The agent still opens a draft pull request, and nothing in the announcement suggests fixes are applied automatically or need less scrutiny. What changes is that a fix you accept may inform future suggestions. That's a reason to reject a sloppy fix outright rather than merging it and cleaning up later.
- Agentic autofix only uses Copilot Memory when Memory is enabled for the user who starts the fix. Organisation and enterprise plans need an admin policy first.
- Both agentic autofix and Copilot Memory are public previews on paid Copilot plans, so behaviour and controls may still change.
- Stored fix patterns are scoped to one repository and can inform Copilot code review and Copilot cloud agent in that same repository.
- Each memory carries code citations that are checked against the current branch before use, and unused memories expire after 28 days.
- Repository owners can review and delete stored facts, so plan a periodic review of what autofix has recorded in sensitive repositories.
- GitHub's published performance gains come from coding agent and code review tests, and none are specific to security fixes yet.
The change is small in the changelog but it links two parts of Copilot that used to work separately. Security remediation now feeds the same repository knowledge that code review and the cloud agent draw on. GitHub's own framing places memory at the centre of a multi-agent Copilot, and adding agentic autofix means a team's security conventions can now be learned, checked and reused across that system. Watch for whether GitHub publishes autofix-specific results or detailed controls as the two features move toward general availability. Until then, teams in the preview should treat the Memory settings page as part of their security review.