

What happened
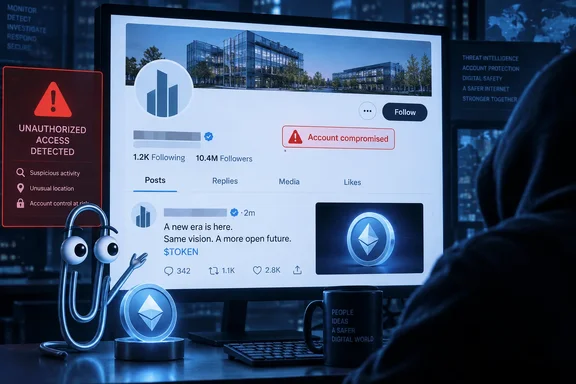
The takeover became visible when @Microsoft started doing odd things. BleepingComputer reported that unknown attackers hijacked the account in what appeared to be a pump-and-dump scheme promoting a crypto token. The account followed @clippymsftcto, an X account impersonating Microsoft's Clippy assistant, and reposted one of its tweets. X has since suspended that account.
NewsBytes reports that the company's profile picture was also changed to a Clippy-themed one during this time. It adds that the posts were later removed, and an unusual "apology" tweet appeared about 30 minutes later before being quickly deleted.
A different account, @ClippyMSFT, was still promoting the $Clippy token after the suspension. It claimed the token has a liquidity pool paired directly with $MSFT. That is the promoter's claim. It is not a verified description of the token, and Microsoft denies any link.
What Microsoft said
Microsoft's spokesperson, named in NewsBytes' report as Brent Colburn, said: "We have confirmed unauthorized access to our account on X including posts that did not come from Microsoft." He also said the account has been secured and the unauthorized posts removed. The investigation is ongoing.
The deleted apology post went further. According to BleepingComputer, Microsoft said it has not authorized, sponsored, endorsed or permitted any crypto token tied to Clippy, Microsoft or $MSFT. It also said it will pursue legal action to have the token and related materials removed. It said it has no affiliation with the token or its creators.
What we don't know
The reporting leaves several things open:
- Access method. Nobody has said how the attackers got in. Phishing, credential theft, SIM swapping and third-party app access are all possible. None is supported by evidence yet, so none should be assumed.
- Losses. No report I reviewed documents victims or financial losses.
- The "pump-and-dump" label. This is BleepingComputer's framing of what the activity appeared to be. The reports include no price or transaction data showing a completed pump-and-dump.
- Scope. There is no indication that anything beyond the X account was affected. That is an absence of reporting, not a confirmed all-clear.
- Wallet drainers. Nothing reviewed says this promotion used wallet-drainer malware or asked users to connect wallets.
A crypto outlet, CryptoBriefing, says the @ClippyMSFT account has discussed liquidity pools reportedly worth over $200,000. That is a reported claim about a promoter's account and is unverified.
Why a real account can still post fake things
The repost came from the genuine @Microsoft account, and that is what gave the promotion its credibility. A verified brand's follow or repost proves nothing if the account has been taken over. Readers should not treat the Microsoft name, Clippy branding, the $MSFT reference or a claimed liquidity pool as a sign of authorization.
Practical takeaways:
- Don't connect a crypto wallet or approve a transaction because a corporate account appeared to endorse a token.
- Look for confirmation on the company's own website or through another official channel.
- Treat any token claiming a tie to a public company's stock ticker with extra suspicion until the company confirms it. Microsoft has explicitly denied this one.
For IT teams, the broader lesson is that social accounts are part of the attack surface. This is general industry guidance, not Microsoft's confirmed remediation, since the breach mechanism is unknown. Strong multi-factor authentication, tight control of who can post, regular review of connected apps, and a rehearsed takedown and communications plan all apply to brand accounts.
Not Microsoft's first brush
BleepingComputer points to earlier incidents:
- Microsoft India, June 2024. Scammers hijacked @MicrosoftIndia, which then had more than 211,000 followers. They used it to impersonate meme-stock trader Keith Gill, known as Roaring Kitty. The account lured people to a fake GameStop crypto "presale" site. BleepingComputer said anyone who connected a wallet and authorized transactions risked having their assets stolen by a wallet drainer. That was a different account and a different lure, and nothing shows the same method was used this time.
- Xbox, 2025. TweakTown reported that Xbox's Instagram and Facebook accounts were used to promote a fake Xbox token. Tom Warren's post describing it dates to about 489 days before this search. It was a different platform and a different Microsoft brand. It shows a pattern of crypto scammers targeting Microsoft's social channels, not a link between the incidents.
- SEC, January 2024. The @SECGov account was compromised by SIM swapping. It was used to post a false Bitcoin ETF approval. BleepingComputer's 2024 report says X's Safety team attributed that breach to SIM swapping and noted that the SEC account did not have two-factor authentication enabled at the time. The hacker, Eric Council Jr., pleaded guilty in February 2025 and was sentenced to 14 months in prison.
None of these cases explains the Microsoft incident. They do show that hijacked, high-trust accounts are a repeat tactic, and that this tactic can move markets.
Bottom line
Confirmed: the account was compromised, unauthorized posts promoted a Clippy token, and Microsoft removed them and denied any involvement. Unconfirmed: the entry point, the token's real ownership, whether anyone lost money, and whether the compromise went beyond X. If Microsoft publishes its investigation findings, those will be the details to watch.
Update: Additional details (October 2, 2026)
According to Pasquale Pillitteri’s report, the takeover lasted about 30 minutes before Microsoft regained control. The impersonating Clippy account reportedly claimed that 500,000 likes would bring the assistant back, using the engagement bait alongside the token promotion.
References
- Microsoft’s X account hacked in crypto pump-and-dump scheme BleepingComputer · 2026-10-02T05:29:56-04:00
- Microsoft's X account hacked to push a Clippy crypto scam - Pasquale Pillitteri Pasquale Pillitteri · 2026-10-02T16:13:00+00:00
- Microsoft India’s X account hijacked in Roaring Kitty crypto scam bleepingcomputer.com