

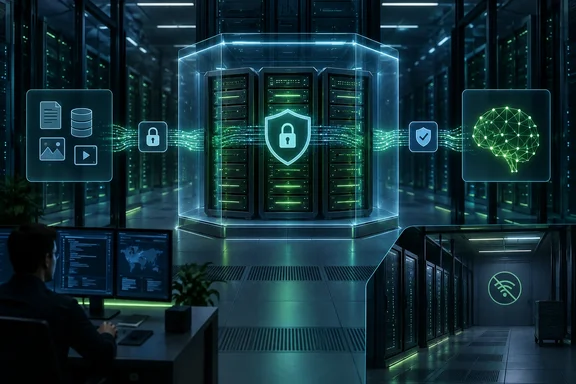
VAST DataEnclave Puts NVIDIA Confidential Computing Inside the VAST DataEngine
VAST started as a storage company and now calls itself an "AI Operating System" company. DataEnclave is the first capability under that label aimed at protecting data while it is being processed. According to Computer Weekly's coverage, Vast DataEnclave uses Nvidia Confidential Computing to create a secure container runtime and attestation service directly within the Vast DataEngine. Models execute inside secure enclaves established through CPU and GPU trusted execution environments. A trusted execution environment (TEE) is a hardware-isolated area of a processor. Code and data inside it are shielded from the rest of the machine, including the host operating system and hypervisor.
VAST's announcement names three target sectors: financial services, healthcare and government. In each of them, moving data to an external AI service is often impractical or not allowed. The company describes the problem as a standoff. Sensitive data can't go to where the leading models run, and model builders won't ship proprietary models into infrastructure they don't trust. DataEnclave's answer is to take the model to the data and let each side check the environment before anything is decrypted.
TechEdt, SecurityBrief Australia and HPCwire all covered the launch. HPCwire's item is VAST's press release reprinted as an "Off the Wire" post, so it confirms the date and wording but isn't independent confirmation. Blocks & Files, SiliconANGLE, Techzine and Computer Weekly add detail from their own reporting, including comments from VAST executives on runtime standards. Blocks & Files also reports that the DataEnclave is supported by on-prem VAST deployments and cloud VAST deployments.
Why GPU Memory Is the Gap Confidential AI Has to Close
VAST's explanation of the technology is simple. Conventional encryption protects model weights while they are stored and while they move across the network. Confidential computing extends encryption and protects data during execution. AI workloads make this harder. During inference, the model weights, prompts and intermediate results sit unencrypted in GPU memory. That memory has historically been outside the protection CPU-based confidential computing provides.
Blocks & Files puts the gap this way: GPUs previously would not typically protect data they are processing, VAST says, unlike confidential (x86) computing which has protected data in CPU memory for a decade. Protecting only the CPU side of an accelerated AI job leaves the most valuable material, the weights and the working data, exposed wherever the actual computation happens.
VAST says DataEnclave closes that gap with confidential virtual machines and containers. It uses NVIDIA Confidential Computing to encrypt guest memory, GPU memory and NVLink traffic while isolating active data and models from infrastructure operators, administrators and other tenants on the same hardware. NVLink is NVIDIA's high-speed GPU-to-GPU interconnect, so the protection is meant to cover multi-GPU jobs as well as a single card. The CPU side still carries a lot of the load. Techzine notes that the Trusted Execution Environments (TEEs) of CPUs from Intel, AMD, and Nvidia form the foundation for the confidential environments that DataEnclave provides.
On hardware, VAST describes NVIDIA Confidential Computing as now in its third generation on Hopper, Blackwell, and Rubin platforms. That tells you which GPU families are involved. It does not give a certified configuration list. The public material doesn't say which server SKUs, CPU generations or firmware levels are supported, and it gives no figures for performance overhead. Those gaps will matter when it comes time to budget for a deployment.
Verify-Before-Decrypt: How DataEnclave Attestation Gates the Keys
The core of the design is what VAST calls verify-before-decrypt attestation. Attestation means the hardware produces signed evidence about what is running on it and in what state, and a separate service checks that evidence against a policy. In the TechEdt report's summary, decryption keys are released only after DataEnclave completes verification of the trusted environment, including NVIDIA GPU attestation.
VAST's technical description lays out the steps:
- A newly deployed confidential VM starts without any keys or credentials.
- The CPU and GPU produce hardware-rooted evidence of the workload's security posture: hardware and firmware state, the software that booted, and the restrictions placed on host actions. The evidence is signed with keys that never leave the hardware.
- The workload sends that evidence to an attestation server, which checks it against the data owner's policy.
- Only if the evidence passes are decryption keys released, so the encrypted model and data can be loaded into the enclave.
This moves trust away from people and onto policy. Normally, a company running a vendor's model on its own servers either trusts its administrators not to copy the weights or doesn't run the model at all. With attestation, the model owner's key service can refuse to release keys to any environment whose measurements don't match what it expects. VAST says administrators and the host stack can't see the unencrypted contents while the workload runs.
These are VAST's stated guarantees. No independent security review or penetration test of DataEnclave has been published. Confidential computing narrows the set of people and software you have to trust. It doesn't make that set zero: the design still depends on the hardware vendor, the firmware and whoever writes the attestation policy.
Split Key Custody, CNCF Trustee and Fortanix Give DataEnclave Its Air-Gap Options
The second design choice is that neither party holds the other's keys. VAST describes Independent Key Control through Bring Your Own Key Management System (KMS) integrations. Customer data keys stay with the customer, and model keys and weights stay in the model builder's trust domain. VAST also says the arrangement covers an enterprise's own fine-tuned weights, not only a vendor's base model. That matters to any organization that has put real money into fine-tuning.
For attestation, there are two routes. SiliconANGLE reports that DataEnclave's attestation services are based on the open-source Cloud Native Computing Foundation Trustee project or can be provided through Fortanix Inc.'s Confidential AI offering. The same report says DataEnclave can be deployed in customer data centers, AI clouds and fully air-gapped environments. VAST presents the Fortanix route as its option for "fully sovereign AI," and Fortanix CEO Anand Kashyap describes his company's contribution as the attestation and key-management layer.
The key-custody model sounds straightforward, but the operational details aren't public yet. The announcement doesn't list supported KMS products, explain how attestation policies are written and versioned, or describe key revocation and recovery. These processes decide whether split custody works in practice or becomes an outage risk when a firmware update changes a measurement and the key service starts refusing releases.
Kata Containers, VAST DataBase Audit Logs and AgentEngine Sandboxes
VAST is building on open standards more than on its own custom runtime. In remarks reported by Blocks & Files, a VAST executive said the company is following and aligning with Kata for the runtime. They noted that Kata was backed by Microsoft, backed by Red Hat, backed by a whole bunch of people in the industry, and that VAST is also aligning around the CNCF's open source project Trustee. Kata Containers is an open-source container runtime that runs each container inside a lightweight VM. For teams already using Kubernetes-style confidential containers, this suggests DataEnclave follows familiar patterns, though VAST hasn't published compatibility details.
For audit, DataEnclave logs attestation events, key releases and enclave lifecycle activity in the Vast DataBase data warehouse. These records provide an audit trail showing which workloads ran and under what policies without revealing the protected data or model weights. VAST calls the trail tamper-proof and queryable. For compliance teams, a record of which model ran against which data and under which verified policy may be as useful as the encryption itself. How the tamper-proofing works hasn't been documented publicly.
The same secure runtime also runs agent sandboxes through VAST AgentEngine. VAST says it enforces policy over which data, systems and tools an AI agent can reach and which actions it can take. The company's argument is that agents aren't accountable the way people are, so they need an identity, a contained runtime and full observability. This is the least detailed part of the announcement. It applies the enclave model to a new kind of workload, and there's no public description yet of how the agent policies are defined.
Sovereign Clouds, Cisco and Supermicro, and the Q1 2027 Ship Date
The partner list shows who VAST expects to buy this. On the model side, SiliconANGLE lists Cohere Inc., CrowdStrike Holdings Inc., Deepgram Inc., The San Francisco AI Factory Inc., Fundamental Research Labs Inc. and TwelveLabs Inc., plus NVIDIA, with Cisco and Supermicro as hardware partners. The quoted executives describe fairly specific uses. CrowdStrike talks about its SafeMind security models running on regulated customers' data. Deepgram describes it as another option alongside its existing self-hosted voice AI. Factory talks about running coding agents where source code can't leave the network. TwelveLabs talks about video models in disconnected environments. Being on the partner list doesn't mean a given model will be available through DataEnclave on day one.
Sovereign and regional AI clouds are the second audience. VAST says that because isolation is enforced in hardware, sovereign and regional AI clouds can establish verifiable trust without dedicating entire machines to a single tenant. In other words, a provider could offer confidential multi-tenant capacity instead of dedicating whole machines to each customer. BUZZ HPC in Canada, Nscale and Sharon AI are named. Sharon AI CEO James Manning says DataEnclave lets his company host frontier models onshore for Australian and Asia-Pacific customers, in environments where both the model weights and the customer's data are protected "from everyone, including us."
OEM partners Cisco and Supermicro are the third channel. Cisco ties DataEnclave to its Secure AI Factory with NVIDIA. Supermicro describes pre-integrated, validated systems that combine NVIDIA Vera Rubin computing, confidential computing and the VAST AI OS, including for air-gapped sites. VAST says DataEnclave is in preview now and will ship in Q1 2027 through VAST and participating OEMs, including Cisco and Supermicro. Pricing hasn't been announced.
What this means for you
For most IT teams, the question now is whether DataEnclave belongs on a 2027 evaluation list, not whether to deploy it. It isn't shipping, it needs recent NVIDIA confidential-computing GPUs and a VAST platform, and its security claims haven't been independently tested. The organizations that should look closely are those blocked from AI adoption by data-residency rules, by fear of administrator access to regulated records, or by model vendors unwilling to self-host. Everyone else can watch for the Q1 2027 release and the first technical write-ups from customers.
- DataEnclave was announced on September 22, 2026, is in preview, and is scheduled to ship in Q1 2027 through VAST, Cisco, Supermicro and other participating OEMs.
- The protection covers data in use: confidential VMs and containers encrypt guest memory, GPU memory and NVLink traffic on NVIDIA's Hopper, Blackwell and Rubin confidential-computing platforms.
- Keys are released only after CPU and GPU attestation passes the data owner's policy, so whoever writes and maintains that policy effectively controls access.
- Customers and model vendors keep separate keys through BYO KMS integrations, but VAST hasn't named supported KMS products or described revocation and recovery, so ask for those before any pilot.
- Air-gapped deployments can use attestation built on the open-source CNCF Trustee project or Fortanix's Confidential AI offering, and attestation and key-release events are logged in VAST DataBase.
- A model partner appearing in the launch doesn't mean its model will be available at launch, so confirm your specific model, GPU generation and performance overhead with VAST or your OEM.
Model builders have been reluctant to ship proprietary weights into infrastructure they don't control. That reluctance has pushed regulated industries toward either sending data to the cloud or doing without the best models. VAST is betting that hardware attestation, split key custody and an auditable runtime can settle that standoff inside a customer's own data center. The approach rests on open components like Kata and CNCF Trustee plus NVIDIA's third-generation confidential GPUs, and it has credible OEM and model partners behind it. The Q1 2027 release will show whether it lives up to VAST's claims: which hardware is certified, how much performance it costs, and whether anyone outside VAST has tested the enclave boundary.