

Microsoft announced the release on September 17 through the Windows IT Pro Blog. The company positions it for widespread endpoint disruptions, time-sensitive jobs, and help-desk surges—situations where a queue of manual Cloud PC requests can become its own business-continuity failure.
But the General Availability label should not be read as “turn it on for everyone.” Reserve is an intentionally constrained emergency-access product, and Microsoft’s own documentation shows that availability, licensing assignment, provisioning readiness, network access, and user policy still determine whether the self-service button produces a usable desktop when an outage actually occurs.
What changes in the Windows App
Before this release, Windows 365 Reserve Cloud PCs were provisioned on demand by IT from Microsoft Intune. The April public-preview announcement described the new self-service option as an Intune-controlled Windows App setting assigned to specific Microsoft Entra ID user groups. General availability changes the release status of that same workflow; it does not remove the administrator from the control plane.
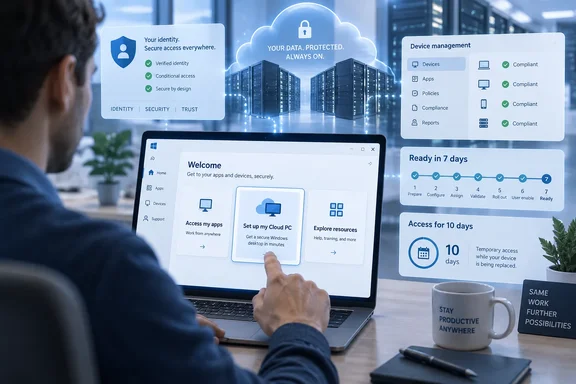
Once enabled for an eligible group, a user whose Reserve Cloud PC has not yet been created sees a Set up my Cloud PC card in the Windows App or web client. Selecting it triggers a confirmation prompt, then begins provisioning. The card changes to show provisioning progress, and the user connects after the Cloud PC becomes available.
The boundary is important for admins designing incident procedures. Users can initiate the creation of an approved Reserve desktop, but they cannot choose an arbitrary configuration, bypass an Intune provisioning policy, create several emergency machines, or convert Reserve into a pool of general-purpose virtual desktops. IT remains responsible for the provisioning policy, group assignments, supported image selection, geography, apps and policy configuration, reporting, and the Cloud PC lifecycle.
Microsoft’s April preview post said the feature is disabled by default and scoped through Windows App settings in Intune. The September General Availability announcement does not state that this default has changed, and the current management documentation continues to describe the setting as off by default and controlled by IT. Administrators should therefore expect a deliberate enablement and assignment exercise, rather than a tenant-wide behavior change arriving automatically.
The documentation still calls the setting “Preview”
There is a paperwork problem in Microsoft’s own published record. The Windows IT Pro Blog calls user-initiated provisioning generally available as of September 17, but the Microsoft Learn page for managing Windows 365 Reserve—last updated August 27—still titles the control “Enable users to provision new Cloud PC instances (Preview)” and includes language saying future availability depends on the results of the public preview.
That is an ordinary documentation lag, not evidence that the announcement is false. Microsoft’s original public-preview post from April 28 and its Windows 365 “What’s new” page both establish that the capability was in preview earlier this year, while the newer Tech Community post explicitly announces General Availability.
Still, it is a meaningful operational discrepancy. A change advisory, internal runbook, or procurement review relying only on the older Learn page could classify the feature incorrectly, and an administrator following the documented portal workflow may still encounter labels that have not been cleaned up to match the new release status.
Microsoft has not yet published a companion General Availability entry in the Windows 365 “What’s new” page, nor has it updated the Reserve management article’s preview heading. Until those records converge, IT teams should retain a copy of the September 17 announcement alongside their deployment records and test the control in their own tenant before treating every portal label as authoritative.
Reserve readiness starts seven days before the incident
The more consequential limitation is not the button in the Windows App. It is eligibility.
Microsoft’s licensing documentation says a user does not become eligible to provision a Windows 365 Reserve Cloud PC until seven days after the Reserve license is first assigned. The same delay applies again after a lapse in coverage. An organization that waits for a laptop fleet incident to buy or assign Reserve coverage cannot expect users to self-provision immediately that afternoon.
That makes Reserve a continuity service that must be staged ahead of time. Microsoft says each covered person needs a Windows 365 Reserve license, along with qualifying Windows 10 or Windows 11 Enterprise, Microsoft Intune, and Microsoft Entra ID P1 licensing. Reserve licenses cannot be pooled or shared between users; unused licenses can return to the tenant’s available pool when a user is removed from a policy, but a license that has already provisioned a Cloud PC remains tied to that user through the license term.
For organizations that intend to use this as a device-outage fallback, the readiness work is therefore more concrete than adding a self-service app tile:
- Assign Reserve provisioning policies and licenses to the intended recovery population well before an incident, then verify that the seven-day eligibility clock has completed.
- Enable the Windows App setting only for groups whose roles, data-access rules, and help-desk processes have been reviewed for self-service recovery.
- Confirm that Conditional Access, multi-factor authentication, application deployment, VPN access, and corporate network dependencies work from an alternate device rather than assuming a managed laptop will be available.
- Train users to recognize that Reserve is a temporary recovery environment and that local files trapped on a failed physical PC will not appear there automatically.
That last point deserves emphasis. A Reserve Cloud PC is not a restored clone of the unavailable device. Microsoft describes it as a preconfigured Cloud PC using corporate apps, settings, and policies. Local data from the failed endpoint is not restored. Teams that want this option to preserve work in a device loss or hardware failure need to enforce cloud-backed storage practices before the emergency occurs.
Self-service does not create reserved capacity
Windows 365 Reserve removes the manual provisioning handoff, but it does not promise that capacity will be waiting.
Microsoft’s Reserve FAQ says the product does not preallocate or guarantee Cloud PC capacity in advance. If the selected geography has limited availability or service-health problems when the request is made, provisioning can fail or wait until capacity is available. The same documentation warns that major disruptions can affect availability through network connectivity, service dependencies, or service load, and says the speed and scale of provisioning vary by tenant and geography.
This is the chief distinction between a convenient self-service recovery path and a fully engineered disaster-recovery guarantee. The workflow can prevent an overwhelmed help desk from becoming the bottleneck. It cannot make a Cloud PC appear if a regional capacity constraint, an identity outage, a connectivity problem, or a dependent Microsoft service is impaired.
Admins should test a small number of real provisioning events under the same geography and policies planned for recovery—not merely sign-in to the Windows App. A test should measure the time from user confirmation to a working session, validate business-critical apps and line-of-business connectivity, and establish how the support team will prioritize users if several groups require access simultaneously. Microsoft recommends prioritizing critical users when multiple provisioning actions are required; self-service makes group targeting and clear eligibility rules more important, not less.
Reserve also has intentionally narrow infrastructure choices. Microsoft documents it as Microsoft Entra-joined on the Microsoft-hosted network, rather than an on-premises domain or custom Azure network connection deployment. Access to line-of-business applications may therefore require a VPN or comparable solution. Organizations whose critical applications assume a particular network path should test that dependency from the Reserve configuration rather than discovering it during a physical-device outage.
Ten days means the Cloud PC must be managed like an emergency asset
A Reserve license provides up to 10 days of Cloud PC access per user per year, and the clock starts once the Cloud PC is provisioned. Microsoft measures use in 24-hour increments; deprovisioning pauses the remaining allowance, while leaving the Cloud PC running consumes days even if the user no longer needs it.
The product does allow both administrators and users to deprovision—or “Return”—the Cloud PC in the Windows App. That convenience carries a recovery risk: deprovisioning deletes the Cloud PC and all data that has not been backed up. Microsoft says there is no grace period, and the management documentation warns that no snapshots are taken when either the admin or user deprovisions the machine.
Reserve Cloud PCs also cannot be treated as endlessly extendable emergency capacity. Microsoft says extensions and license stacking are not supported at General Availability. When a user exhausts the 10-day allocation, the service takes a retention snapshot before deprovisioning, but that user cannot provision the Reserve Cloud PC again because their permitted access has expired.
The best use case is therefore bounded interruption recovery: an employee whose laptop has failed, been lost, is awaiting replacement, or is caught in a broader endpoint incident. It is a poor fit for an open-ended remote-work substitute or a way to postpone a deeper desktop replacement, repair, or standard Windows 365 deployment decision.
Microsoft has made the recovery trigger faster, and for a prepared tenant that could save hours during a device incident. The remaining work is administrative: assign coverage early, validate the alternate-device route, keep critical data in services that follow the user, and make sure the people allowed to self-provision understand that their Reserve desktop is temporary—and that its 10-day clock begins the moment they create it.