

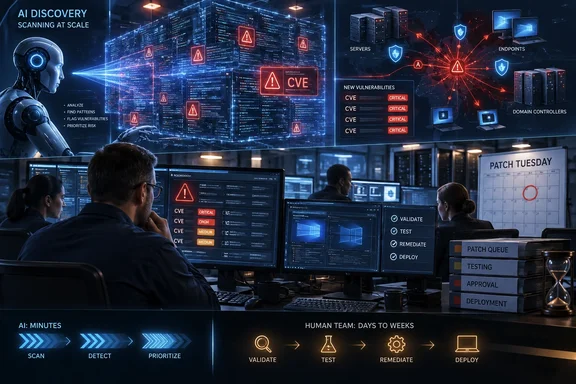
As reported by The Register from Gartner’s IT Symposium on Australia’s Gold Coast, Lawson expects the surge in AI-discovered flaws to retire technical debt and eventually reduce the number—or at least severity—of newly disclosed vulnerabilities. Gartner confirms that Lawson spoke in a September 15 session explicitly framed around separating the reality of Mythos from the hype. His forecast is plausible, but it is a forecast, not evidence that the backlog is close to cleared.
For Windows administrators, the practical danger is treating a lower future CVE count as proof that risk has fallen. The September 2026 Patch Tuesday shows why: the issue is no longer simply finding defects. It is deciding which of hundreds of findings can threaten a real environment, then getting tested fixes onto Windows endpoints, servers, identity systems, and line-of-business applications before an attacker can turn public patch information into an exploit.
Gartner’s 2027 prediction depends on a cleanup that has not been measured
Lawson’s theory is straightforward. Massive, established products accumulated decades of code, much of it written before today’s secure-development practices and modern compiler protections. If AI code auditors can examine those codebases at a depth and speed that human researchers could not sustain, vendors may be finding a one-time concentration of old defects. Fix enough of them, the argument goes, and future releases should contain fewer high-impact bugs.
Anthropic’s own Project Glasswing announcement supports the first half of that argument. The company said in April that its unreleased Claude Mythos Preview had found thousands of high-severity vulnerabilities, and that Microsoft was among the launch partners using the system for defensive work. Anthropic also said it had extended access to more than 40 organizations building or maintaining critical software.
What has not been shown is the point at which a mature codebase becomes substantially “cleaned up.” Security defects are not a finite pile of isolated mistakes. New features create new attack surfaces; refactoring can introduce regressions; dependencies change; configurations expose code that was previously unreachable. A reduction in disclosed CVEs could mean vendors have eliminated classes of old bugs. It could also mean disclosures are delayed, triage teams are overwhelmed, findings are bundled differently, or the research focus has moved elsewhere.
Anthropic’s coordinated-disclosure dashboard makes that distinction unusually clear. The company says Mythos and other Claude models generate candidate vulnerabilities first; those candidates then need human reproduction, severity assessment, and written reports before maintainers receive them. Anthropic acknowledges that some genuine bugs have been confirmed but have not yet been reported because of capacity limits. It also calls the number of patches created a more reliable measure of impact than its own true-positive figures—while noting that patches are a lagging indicator because they take time to develop.
That is the material constraint missing from the sunny version of the 2027 forecast. Discovery throughput is not remediation throughput. An AI system can find ten times as many suspicious paths through a codebase, but it cannot by itself decide whether a proposed fix breaks an enterprise deployment, invalidates a support matrix, disrupts a domain controller, or creates an outage in a hospital.
September’s Microsoft totals show why CVE counts are a poor workload metric
The scale of Microsoft’s September 2026 release is real, but even the public totals demonstrate how slippery a single patch-count headline can be. TechRadar reported 974 fixed vulnerabilities, citing Microsoft release notes. Trend Micro’s Zero Day Initiative counted 972 new Microsoft CVEs, then put the total at 997 after including external and Chromium-related issues. The Register characterized the release as more than 970 patches.
Those figures are not necessarily contradictory. They appear to use different inclusion rules: whether externally assigned CVEs are counted, whether browser issues are folded in, and whether product-level advisories are treated as distinct from underlying vulnerabilities. But they do establish an important operational point: an organization should never build its monthly risk posture around a headline number.
Zero Day Initiative’s September review identified 114 Critical CVEs in the broader Microsoft tally and called out patches spanning Windows, Office, Exchange Server, SQL Server, Active Directory, Remote Desktop, DHCP, DNS, Hyper-V, Windows Hello, Defender, Azure services, and other products. The firm highlighted two Windows elevation-of-privilege vulnerabilities listed as exploited in the wild and separately urged rapid attention to server-facing issues such as Exchange, SharePoint, Remote Desktop Services, DHCP, and DNS.
A Windows estate does not inherit 974 equally urgent tasks merely because Microsoft issued 974 CVEs. An organization without on-premises Exchange, internet-facing SharePoint, DHCP servers, or Remote Desktop Services has a different exposure profile from one running all of them. Conversely, a single actively exploited flaw on an exposed management server can outweigh hundreds of endpoint fixes with no realistic attack path in that environment.
The count also obscures packaging. A large advisory may result in one cumulative Windows update, a Microsoft 365 servicing change, an Edge channel update, or a product-specific server update that requires maintenance planning. For endpoint administrators, the operational question is whether the security update reaches the supported Windows build and whether it installs successfully. For server teams, the question is whether the deployment can be tested and scheduled before the exposure window becomes unacceptable.
Microsoft’s own AI backlog is the warning, not the reassurance
The strongest evidence against assuming an imminent lull comes from Microsoft’s reported experience with Mythos itself. In July, ProPublica reported from internal Microsoft recordings and documents that Mythos Preview was finding flaws faster than Microsoft could patch them. The report said a single April scan of SharePoint identified 90 issues classed as critical and 141 marked important, with further findings in May.
That is a single-outlet report and Microsoft has not publicly supplied a complete accounting of the findings, their final severity, their affected products, or their remediation status. Still, it fits Anthropic’s public description of a disclosure process constrained by human triage and patch production. It also makes Lawson’s prediction conditional on something far harder than bug discovery: vendors must sustain a rate of verified, safe fixes that exceeds the rate at which AI-assisted tooling uncovers valid defects.
Anthropic’s technical materials underline the urgency. The company says Mythos Preview can help turn known, already-patched vulnerabilities—N-days—into working exploits. That matters because public disclosure and patch releases do not eliminate exposure on systems that have not yet been updated. The company’s own framing is not that defenders have years to absorb the change; it is that attackers may use AI to compress the interval between a patch becoming available and exploitation beginning.
For defenders, a mountain of findings therefore has two different meanings. It can represent technical debt being removed before attackers reach it. It can also represent a widening queue of issues whose existence is known to sophisticated researchers, vendors, maintainers, and eventually adversaries. The difference is determined by the time from discovery to deployed mitigation—not the annual CVE total.
Patch operations need to be built around exposure, not volume
CISA has already shifted its federal guidance in this direction. Its Binding Operational Directive 26-04, issued June 10, requires federal civilian agencies to prioritize vulnerabilities using asset exposure, Known Exploited Vulnerabilities status, exploit automation, and likely post-compromise impact. CISA explicitly warns that AI may shorten the time between patch release and potential exploitation.
Private organizations are not bound by that directive, but its model is useful for Windows and enterprise IT teams dealing with AI-inflated patch volumes. A defensible queue should answer four questions before it asks how many CVEs arrived this month:
- Is the affected system publicly exposed, reachable from a partner network, or otherwise on a realistic attacker path?
- Is there evidence of active exploitation, especially a CISA Known Exploited Vulnerabilities listing or credible threat intelligence?
- Can exploitation be automated or chained with commonly available access?
- Would successful exploitation lead to domain compromise, remote code execution, credential theft, data access, or meaningful operational disruption?
That means tag accuracy and asset inventory become more important, not less. A vulnerability scanner that cannot distinguish a retired Windows Server from a production DNS server, or an unexposed SQL instance from one reachable through a public application path, creates noise at precisely the moment defenders need prioritization.
It also means security leaders should stop rewarding teams chiefly for ticket closure. Lawson’s suggestion, reported by The Register, to measure the business outcome is correct: keeping a hospital, factory, payment system, or identity service operating is more meaningful than processing an impressive number of findings. But that result depends on giving teams the authority to defer low-risk work, expedite exposed systems, and use compensating controls where a patch cannot be installed immediately.
A virtual patch, such as a temporary firewall restriction, reverse-proxy rule, application control, or service isolation measure, can buy time. It is not a substitute for a vendor-supported fix, and it must have an owner and expiration date. AI can help draft an F5 iRule or query language, as Lawson suggested, but an administrator still needs to verify that the control blocks the exploit path without taking down legitimate traffic.
The 2027 metric that will matter
Gartner’s optimism will be justified only if the industry can show that AI-assisted discovery is producing fewer exploitable defects and that the remaining ones move from identification to deployed remediation faster than attackers can operationalize them. A raw decline in CVE volume will not prove either proposition.
For now, September’s Microsoft release is evidence that the discovery side has accelerated. The immediate response for Windows and enterprise administrators is to make exposure-aware triage, tested deployment rings, accurate asset tagging, and exception tracking faster than their monthly vulnerability intake. If Mythos makes 2027 easier, it will be because that remediation machinery caught up—not because the CVE counter happened to fall.