

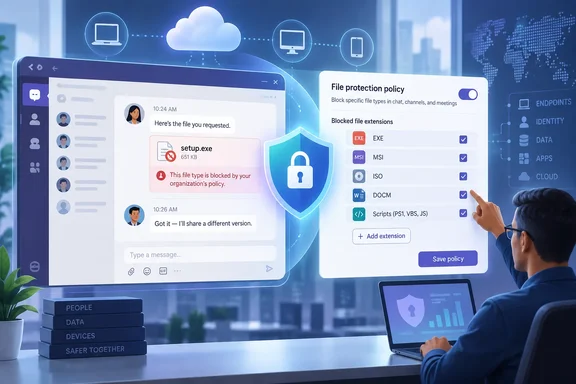
The change addresses a limitation that Microsoft’s own Teams documentation still states plainly: the current blocked-extension list is not configurable by administrators. Today, an organization can enable or disable the file-type check, but it cannot tune the types that trigger it. That has left security teams choosing between Microsoft’s preset list and removing the protection entirely when a legitimate workflow depends on a blocked format.
For Teams administrators, the practical consequence is straightforward: November’s planned update could make the protection usable in organizations that previously found the default too restrictive. It does not, however, turn Teams into a content-inspection system or an endpoint execution control. Microsoft’s current documentation describes the feature as an extension-based block, which means the new flexibility should be treated as one layer in a larger control set rather than a substitute for Defender, App Control, or attachment scanning.
What Teams blocks today
Weaponizable File Protection blocks a Teams message when an attachment uses an extension Microsoft has classified as potentially dangerous. Microsoft Learn says the check applies in chats and channels: Teams identifies the blocked extension, prevents delivery of the entire message and attachment, tells the sender why it was stopped, and lets that sender remove the file and resend the message.
The current list is broad. It includes familiar Windows execution and scripting formats such as .exe, .msi, .cmd, .bat, .dll, .lnk, .reg, .scr, .vbs, .js-adjacent script formats such as .wsf and .wsh, and Visual Basic script extensions. It also covers disk and archive formats including .iso, .img, .cab, .ace, .arj, .xz, and .z; mobile or other-platform packages including .apk, .deb, and .appx; and macro-enabled Office-related formats such as .docm, .xll, .ppa, and .ppam.
The breadth explains why the setting can create friction outside an office-document workflow. Software teams may exchange scripts, installers, libraries, package files, registry changes, or signed internal utilities. IT departments may need to pass a diagnostic archive or an installer to a user. A product or engineering group might have a defensible reason to use one of the extensions that Microsoft blocks globally, even where the organization’s security controls can safely govern it elsewhere.
Under the present design, the response was binary: leave the full Microsoft list enabled or turn off the file-type check. The roadmap item promises a third path, allowing a tenant to keep Microsoft’s recommended defaults or customize the extensions blocked by Teams.
A default-on control now meets real-world exceptions
This is arriving after Microsoft made the underlying protection a more consequential baseline setting. Microsoft’s January 2026 Message Center notice said Weaponizable File Protection, malicious URL protection, and false-positive reporting would be turned on by default for Teams tenants that had not previously changed their messaging-safety configuration. Organizations that had saved their own settings kept those settings.
The earlier rollout was also wider than the new roadmap’s desktop label might suggest. Microsoft’s original deployment notice said the file protection applied to Teams for Windows and Mac desktop, web, iOS, and Android, while the current Teams Learn page describes the protection as applying to Teams messages generally. Roadmap 571298, by contrast, names Desktop as its platform. Microsoft has not said whether that label means the customization interface will initially be available only when administered for desktop clients, whether enforcement will be desktop-only at launch, or whether mobile and web clients will honor the same tenant policy from day one.
That omission matters. A tenant-level messaging policy that behaves differently by client would be difficult to explain and harder to operate. But a roadmap platform field is not a technical specification, and administrators should not assume client parity until Microsoft publishes the supporting Teams Admin Center documentation or a Message Center rollout notice.
Microsoft also has not said whether admins will be able only to add extensions to its default deny list, remove items from it, replace the list entirely, or create scoped policies for distinct user populations. Those choices determine whether this is a modest exception-management feature or a substantial shift in the security model.
Extension blocking has a hard technical boundary
The key caveat is in Microsoft’s current technical description: Teams scans messages for weaponizable extensions. Microsoft Learn explains the process in terms of identifying file names with blocked extensions, and a Microsoft Q&A response published through Learn says the existing capability blocks files on their extension rather than MIME type or the underlying file content.
That makes the feature useful as a policy guardrail, but it also defines what it cannot prove. An extension block can prevent casual transmission of a plainly named executable or script through a chat. It cannot establish that every file with an allowed extension is safe, and it should not be expected to stop every delivery technique an attacker may attempt. A malicious payload can be embedded in a permitted document type, delivered through a link, compressed or otherwise repackaged, or renamed in ways that move the risk into another layer of the collaboration stack.
Teams administrators should therefore avoid treating the future custom list as an opportunity to build a sprawling, bespoke malware taxonomy. The strongest use is likely narrower: retain the Microsoft baseline, document justified exceptions, and add a limited number of organization-specific extensions that should never be exchanged in Teams.
For Windows environments, endpoint controls remain decisive after a file reaches a device. Microsoft Defender for Endpoint, Microsoft Defender for Office 365 where applicable, Attack Surface Reduction rules, Windows App Control, Smart App Control in supported consumer scenarios, and application allowlisting policies address different parts of the chain. Teams’ file-type check stops a message before delivery; it does not replace the policies that decide whether an attachment can execute, load a library, invoke a script host, or establish persistence on a Windows machine.
External chats can make one tenant’s decision everyone’s problem
Microsoft’s Teams documentation contains another operational detail that becomes more important if file lists are customized. In external collaboration, Microsoft says that if any organization participating in a conversation has file protection enabled, it applies to everybody in that conversation. A message with a blocked type is stopped for all participants.
That model is sensible for preventing a less restrictive tenant from becoming a route around another participant’s policy. It also means an organization’s custom additions can disrupt shared work with suppliers, customers, managed-service providers, or partner engineering teams. The blocked message does not merely hide the attachment: recipients cannot access the original message content either.
Help desks will need to know that distinction. A user may report that “Teams ate my message,” when the immediate cause was a blocked attachment included alongside ordinary text, instructions, or a support request. The sender can edit and resend without the disallowed file, but the receiver does not get the original text automatically.
Before the rollout, Teams owners should identify workflows built around files that overlap with the existing list. This is particularly relevant for software deployment, device management, desktop support, engineering, and security operations teams. The review should cover both internal Teams channels and external chats, because a policy tuned for internal support may create unexpected failures at a partner boundary.
What administrators can do before November
There is no new setting to configure yet; Roadmap 571298 remains marked In development. The useful preparation is to establish a baseline now, while the old behavior is still documented and predictable.
- Review the current Teams Admin Center setting under Messaging settings and Messaging safety, where Microsoft exposes “Scan messages for file types that are not allowed.”
- Record whether the protection is enabled and whether the tenant relied on the January 12, 2026 default-on change or had previously saved a custom messaging-safety configuration.
- Inventory support tickets and user workarounds involving blocked Teams attachments, especially files shared by endpoint management, developers, and external partners.
- Decide in advance who can approve a future exception to Microsoft’s default extension list, and require a business owner, expiry date, and compensating endpoint control for each exception.
- Update support guidance so staff understand that a blocked attachment can also block the accompanying Teams message text.
Microsoft has announced the destination but not yet the controls that will get administrators there. The November 2026 release is promising because it removes an unnecessarily blunt choice between a vendor-maintained list and no Teams file-type protection at all. Until Microsoft documents whether the list can be narrowed, expanded, replaced, or scoped, the safest planning assumption is to preserve the recommended baseline and use customization sparingly.