

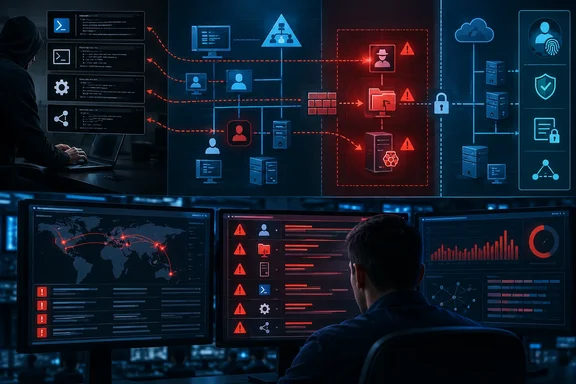
The September 16 CISA publication frames cyber decoys as assets made to appear useful or valuable to an attacker while serving three defensive purposes: distracting an intruder, producing an alert when the asset is accessed, and collecting threat intelligence. CISA explicitly ties the strategy to Zero Trust, whose practical premise is that an attacker may already have some degree of access. In other words, this is guidance for detecting post-compromise behavior, not a substitute for preventing the initial breach.
That distinction deserves emphasis. A decoy domain-admin account will not stop password theft. A fake file share will not patch a vulnerable VPN appliance. But an access attempt against either can cut through the ambiguity that makes an intrusion using valid Windows credentials so difficult to separate from normal IT activity.
CISA’s release is itself authoritative on the new guidance, although its public landing page currently provides only the high-level description and notes that the document is still awaiting Section 508 accessibility completion. No independent outlet had published additional technical detail on the new document at the time of publication. The important reporting context comes from CISA’s earlier multi-agency work on living-off-the-land activity and from deception research: decoys work best when they are engineered as monitored tripwires within a real detection-and-response process, rather than treated as unattended traps.
Decoys are meant to expose the activity EDR often cannot classify
CISA’s 2024 joint guide on living-off-the-land techniques described a familiar Windows enterprise problem: adversaries exploit trusted native binaries and administrative tooling because those tools are already present, signed, and routinely used. PowerShell, PsExec, ntdsutil.exe, WMI, Remote Desktop, scheduled tasks, and management agents may all have valid operational purposes. A security product that simply blocks all of them would also block the work of an IT department.
The problem becomes more acute after an intruder gains a user or service account. They may query Active Directory, enumerate shares, test remote administration paths, discover privileged users, and move laterally with little malware to scan for. Default logging frequently lacks the command-line, authentication, directory-service, and network context needed to decide whether those actions are expected.
A decoy changes the signal-to-noise ratio. A fabricated credential in a place an attacker is likely to search, a bogus administrative share, or a deliberately unused server account has no legitimate business workflow. If someone tries it, the alert can be treated as high priority from the outset—provided the organization has genuinely kept that object out of normal administration.
This is why “cyber decoy” is broader than the old image of an internet-facing honeypot. CISA’s description includes fake systems, accounts, and data. For a Windows-heavy organization, the lower-risk and more useful starting point may be an identity or data decoy rather than a full, interactive fake Windows Server host.
Active Directory is the obvious Windows deployment point
CISA’s living-off-the-land guidance says its incident responders and red teams predominantly encounter this tradecraft in Windows environments, reflecting Windows’ place in corporate networks. It also warns that common administrative binaries are too often available to all users or protected by broad exceptions because administrators need them.
That creates a direct use case for deception around Active Directory and privileged access. A practical decoy program should focus on places where an attacker conducts discovery or reaches for privilege—not on inventing a fake environment that bears no resemblance to the production network.
Useful examples include:
- A disabled or tightly controlled decoy account that resembles an administrative identity but is never assigned to routine tasks, never used for scheduled jobs, and is monitored for authentication attempts, group-membership lookups, password-reset activity, and Kerberos ticket requests.
- A honeytoken credential placed only where a malicious operator conducting credential discovery might encounter it, with immediate alerting if the credential is used or tested.
- A non-production file share containing clearly fictitious but plausible business data, configured so that reads, writes, copies, archive operations, and unusual access paths become security events rather than ordinary file-server noise.
- A decoy host or service built with strict network segmentation and no pathway to production assets, where connection attempts, service enumeration, and authentication requests flow into the organization’s SIEM.
The trap must fit the local environment. A “legacy payroll server” decoy placed in a company that has no payroll systems on-premises is likely to be ignored or quickly recognized as artificial. A fake high-value account with a naming convention that does not match the organization’s account standards can create the same problem. Realism is not cosmetic; it determines whether the decoy will be encountered during authentic discovery activity.
MITRE’s guidance for security operations centers has similarly highlighted Active Directory deception, including decoy objects and fictitious privileged accounts that attackers can discover through directory queries. Research summarized by USENIX also finds that modest decoys and honeytokens can function as early-warning mechanisms, while high-interaction honeypots require far more effort to keep believable, current, and safely contained.
A decoy is only useful if the alert has an owner
The operational gap in many deception deployments is not deployment—it is response. Teams install a lure, send events to a SIEM, and then discover weeks later that access alerts were buried alongside vulnerability scans, inventory agents, red-team activity, and misconfigured scripts.
CISA’s new document is explicitly about detection and response. Administrators should therefore decide the response path before creating any decoy asset. A high-confidence interaction should have a named queue, a severity level, evidence-retention requirements, and a documented rule for when to isolate a device, revoke a session, suspend an account, or begin incident handling.
For Windows environments, responders need enough telemetry to answer basic questions quickly:
- Which user, service account, source IP address, endpoint, and process initiated the interaction?
- Was the attempt interactive, remote, scripted, scheduled, or generated by an approved management platform?
- Did the same identity conduct unusual LDAP, SMB, WinRM, RDP, PowerShell, or Kerberos activity before or after touching the decoy?
- Is the device attempting broader discovery, remote execution, credential dumping, or connection to systems outside its expected administrative scope?
This is where the new CISA guidance should be read alongside the agency’s existing SIEM and SOAR implementation material. A decoy alert without correlated endpoint, identity, network, and cloud audit logs identifies a suspicious touch; it may not tell responders whether the event is an isolated scan, a compromised admin workstation, or an active lateral-movement attempt.
The response plan also needs an exception process. Security teams must know about legitimate vulnerability scans, asset inventories, backup services, red-team exercises, and major configuration-management changes before those tools touch decoys. The goal is not to excuse alerts after the fact. It is to keep decoys sufficiently isolated and clearly documented that the rare alert remains meaningful.
High-interaction decoys carry real containment obligations
The attractive part of deception technology is its promise of high-fidelity intelligence: allow an intruder to interact with a fake asset and observe commands, malware, tooling, and persistence methods. The cost is that a realistic host can become a real operational risk if it is not isolated.
CISA’s earlier federal incident-response playbooks recognize honeynets, honeytokens, and fake accounts as active-defense capabilities, but they pair the concept with the need to protect the wider enterprise. A high-interaction Windows decoy should never have trusted network paths, reusable production credentials, access to sensitive shares, or permissive outbound connectivity that could turn it into an attack relay.
For most organizations, that makes a layered deployment the sensible route. Begin with low-interaction decoys and tokens that produce a clean alert: fake credentials, monitored directory objects, restricted shares, and unused service endpoints. Validate the telemetry and incident workflow during tabletop exercises and authorized red-team testing. Only then consider more elaborate decoy hosts designed to capture extended attacker behavior.
This also avoids the common mistake of treating a deception platform as a replacement for hardening. CISA’s living-off-the-land guidance still calls for detailed centralized logging, behavioral baselines, least privilege, application allowlisting where feasible, segmentation, and strong authentication controls. A decoy detects a wrong turn; those controls reduce the number of routes an attacker can take.
The measure of success is response time, not the number of traps
CISA’s release provides a useful corrective to the idea that Zero Trust ends with identity verification at the network edge. If a malicious actor acquires an authenticated session, defenders still need mechanisms that reveal abnormal discovery, lateral movement, and access attempts inside the environment. Decoys provide one of the few detection methods where the intended event is inherently suspicious.
For IT teams, the first milestone is modest: identify one privileged-access path, one sensitive data path, and one likely discovery behavior that currently produce too much ambiguous telemetry. Place decoys there, route the events to the SOC, and rehearse the escalation.
The outcome CISA is pushing for is not a more elaborate fake network. It is a faster, more confident response when a real intruder starts behaving like an intruder inside a Windows estate.