

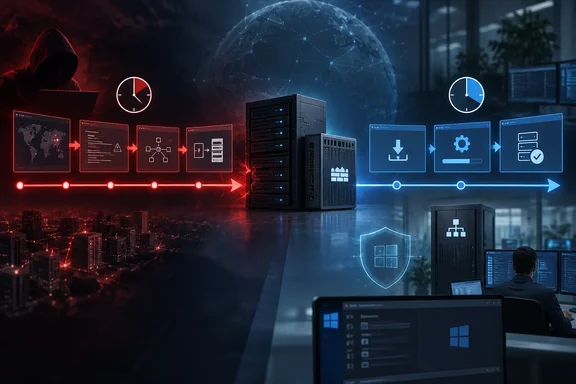
The 2026 Microsoft Digital Defense Report, released October 1, says the median time between a vulnerability being discovered in the wild and its weaponisation has fallen to well below 24 hours, while organisations can take between 30 and 60 days to remediate critical externally facing vulnerabilities, creating what the company described as a widening window of opportunity for attackers. Microsoft's security blog followed up on October 6 with advice for CISOs. That post gets specific about domain controllers, edge devices and Patch Tuesday volume, which matters a lot to anyone running Microsoft software on-premises.
Here's what the report measured, what it didn't, and what IT teams can do this week.
The headline numbers, read carefully
Irish Tech News reports that the findings draw on threat activity observed between 1 July 2025 and 30 June 2026. Within that window, Microsoft makes three claims that matter most to Windows and enterprise readers:
- Weaponization under a day. This is the median time from discovery "in the wild" to a usable attack. Weaponization means turning knowledge of a bug into something an attacker can run: exploit code, a scanning workflow, or an intrusion chain aimed at exposed systems.
- Remediation in 30–60 days. This covers critical vulnerabilities on externally facing systems such as gateways, identity services, web apps and remote-access products.
- Many more disclosures. Nearly 40,000 Common Vulnerabilities and Exposures (CVEs) were published during the first half of 2026 alone, according to Microsoft. On its public report page, Microsoft says the year is on track to roughly double, and that these counts include only publicly reported vulnerabilities. remio's companion coverage says the company projects roughly 72,000 disclosures for the full year.
There are limits to these numbers. Microsoft's public summary doesn't give an exact median in hours, a sample size, a distribution, or a detailed method for the weaponization figure. A median says nothing about the extremes. Some flaws take weeks to weaponize, and others are exploited before the vendor understands them. An authentication bypass and a memory-corruption bug that needs a reliable exploit chain are very different jobs for an attacker.
The 30–60 day range isn't universal either. Cloud services can sometimes push mitigations within hours, while regulated or industrial environments often need more testing. The numbers are best read as a planning signal, not a countdown for every CVE.
One analysis on Pebblous's blog adds a detail worth knowing. It notes the median is measured from discovery in the wild, not from public disclosure. That matters, because a clock that starts at discovery can run before most defenders have even heard of the flaw. The same analysis argues that the bottleneck the report names is not the patch but knowing which assets are exposed.
Section summary: Microsoft reports a real, large mismatch in timing. Treat the exact figures as vendor telemetry with an unpublished method, not a law of physics.
How AI is changing the attack chain
Microsoft says AI is now used at most stages of an attack. As Digit summarized, the report describes AI being used across vulnerability discovery, reconnaissance, phishing, malware and exploit development, data analysis and post-compromise activity.
The report also describes a shift over the past six months. AI went from helping human operators, to directing attack activity, toward running parts of attacks on its own. It cites a frontier AI model that chained together 32 attack stages, but that was in a controlled evaluation, not a live network. Pebblous reports the original evaluation shows completion in only 2–3 runs in 10 on that 32-step chain. We couldn't confirm that figure against Microsoft's full report, so treat it as one outlet's reading.
Microsoft is also clear that fully autonomous attacks aren't the norm yet. Most complex real-world intrusions still involve meaningful human direction. Byte Journal noted the company's narrower framing: threat actors are using AI but that most of it still sits inside parts of attack workflows that already existed, and that the methods underneath are the familiar ones.
In practice, AI saves attackers time in a few specific places:
- Patch diffing. Comparing patched and unpatched code to find the fix and work out the bug is an old technique. Models can now automate much of the reading and the proof-of-concept writing.
- Reconnaissance. Models can quickly connect scattered public records, software fingerprints and documentation.
- Social engineering. Phishing lures can be tailored, translated and varied at scale.
- Post-compromise triage. Once inside, an operator can have a model sort files, explain scripts and suggest the next move.
The usual weak points still matter most. In Microsoft Defender Experts data, user execution accounted for 30% of observed initial access and valid accounts for another 20%. Among detections tied to the five leading CVEs Microsoft analyzed, 58% involved CVE-2020-1472, a Netlogon flaw ("Zerologon") first disclosed in 2020. If a six-year-old domain controller bug still leads the detections, faster exploit tooling is only part of the problem.
Section summary: AI shortens the attacker's research and setup time. The weak points it exploits are still identities, exposed services and old unpatched systems.
Why defenders can't simply match that speed
Attackers can try thousands of targets and accept failures. Defenders have to keep systems running, pass change review, and make sure a patch doesn't break payroll. Byte Journal reports Microsoft's view that remediation is structurally slower than discovery, because many systems lack the unit and integration testing that would let code changes ship quickly. Microsoft concludes the world likely faces a multi-year period in which the number of known but unpatched vulnerabilities rises sharply.
AI also adds work for defenders. Microsoft's October 6 CISO post says most vulnerabilities in its cloud software are mitigated by Microsoft without customer action. On-premises software is another matter. Microsoft tells customers to expect far more vulnerabilities in Patch Tuesday releases than before frontier AI models arrived, and says September 2026 set a record of close to 1,000. That figure covers Microsoft's monthly security updates, not industry-wide CVE counts. Even so, it means much more testing and deployment work for any WSUS, Intune or Configuration Manager team.
The same post explains that AI models are nondeterministic: repeated runs of one model, or runs of different models, can produce different findings. Microsoft says it wraps its models in a "harness" layer that controls code access, validates outputs and feeds findings into triage and remediation. One of these harnesses, codenamed MDASH, is now available to customers.
Section summary: Faster discovery helps only if triage, testing and deployment keep pace. On-premises Microsoft admins should plan for more patches every month.
What Microsoft tells CISOs to do
The October 6 guidance is the most actionable part of this story. Microsoft recommends:
- Patch critical systems within 24 hours. Microsoft names domain controllers and edge devices, which have traditionally been patched during weekends or holiday windows. It suggests deploying fixes to them within 24 hours instead of waiting for the next maintenance window. This is advice, not a guarantee that every update can safely ship that fast.
- Put more resources into on-premises patching, including prioritization and timing, because Microsoft expects high Patch Tuesday volumes to continue.
- Scan your own code now with harness-based tools, without waiting for access to frontier models, and budget for both tokens and human triage.
- Invest in defense in depth and monitor the health of critical controls, because not every vulnerability will be patched in time.
One discrepancy: Pebblous says the report itself recommends 72 hours; the US federal deadline is 7–14 days. We couldn't confirm the 72-hour figure against Microsoft's report text. The CISO post's 24-hour advice applies only to the most critical systems. Don't read either number as a blanket service-level target.
A practical exercise for Windows shops
Microsoft's own advice favors measuring exposure reduced and time to mitigation over counting patches. Here's a simple way to test your program against the new timeline. This is editorial advice based on general practice, not a Microsoft requirement:
- Pick a recent critical flaw that affected your estate, such as a Windows Server, Exchange, or edge appliance CVE.
- Rebuild the timeline: when you learned of it, when you identified the affected assets, when you applied an interim mitigation, when you patched, and when you verified the fix.
- Ask how long the vulnerable service was reachable, not just whether the patch met policy.
- Find the blockers: asset inventory gaps, unclear ownership, change approval, or a lack of test coverage.
- Decide your interim options in advance: restricting access, isolating a host, rotating credentials, or adding detections. These buy time but don't replace patching.
If step 3 takes weeks, you're well behind the timeline Microsoft describes.
The skeptic's corner
Microsoft sells security products, threat intelligence and AI-assisted defense tools, so it benefits from describing security as a contest at machine speed. That doesn't invalidate telemetry gathered from its huge customer base. It does mean readers should keep measured observations separate from product pitches. Microsoft's view is also shaped by customers who rely heavily on its products, so it isn't a neutral census of every network.
What would settle the debate? Clear definitions of what counts as "weaponization," published distributions, and similar figures from other large telemetry providers. Until then, the direction is clear even if the exact numbers aren't. The window between a flaw becoming known and being used is shrinking, and a patch cycle that runs on the calendar won't keep up.
References
- Microsoft AI Vulnerability Weaponization Is Outrunning the Patch Cycle - remio remio · 2026-10-05T16:27:57.025000+00:00
- Microsoft Digital Defense Report 2026: AI Is Accelerating Both Sides of the Cybersecurity Race remio.ai
- 2026 Digital Defense Report | Security Insider microsoft.com